> ## Documentation Index
> Fetch the complete documentation index at: https://docs.ravenna.ai/llms.txt
> Use this file to discover all available pages before exploring further.
# Manage SSO
> Edit, disconnect, or delete your Ravenna SSO connection, replace an expiring SAML certificate, enforce SSO-only sign-in, and monitor sign-in activity.
After you [set up SSO](/integrations/sso/setup), manage the connection from **Settings > SSO**. You need organization admin access.
## Check the connection status
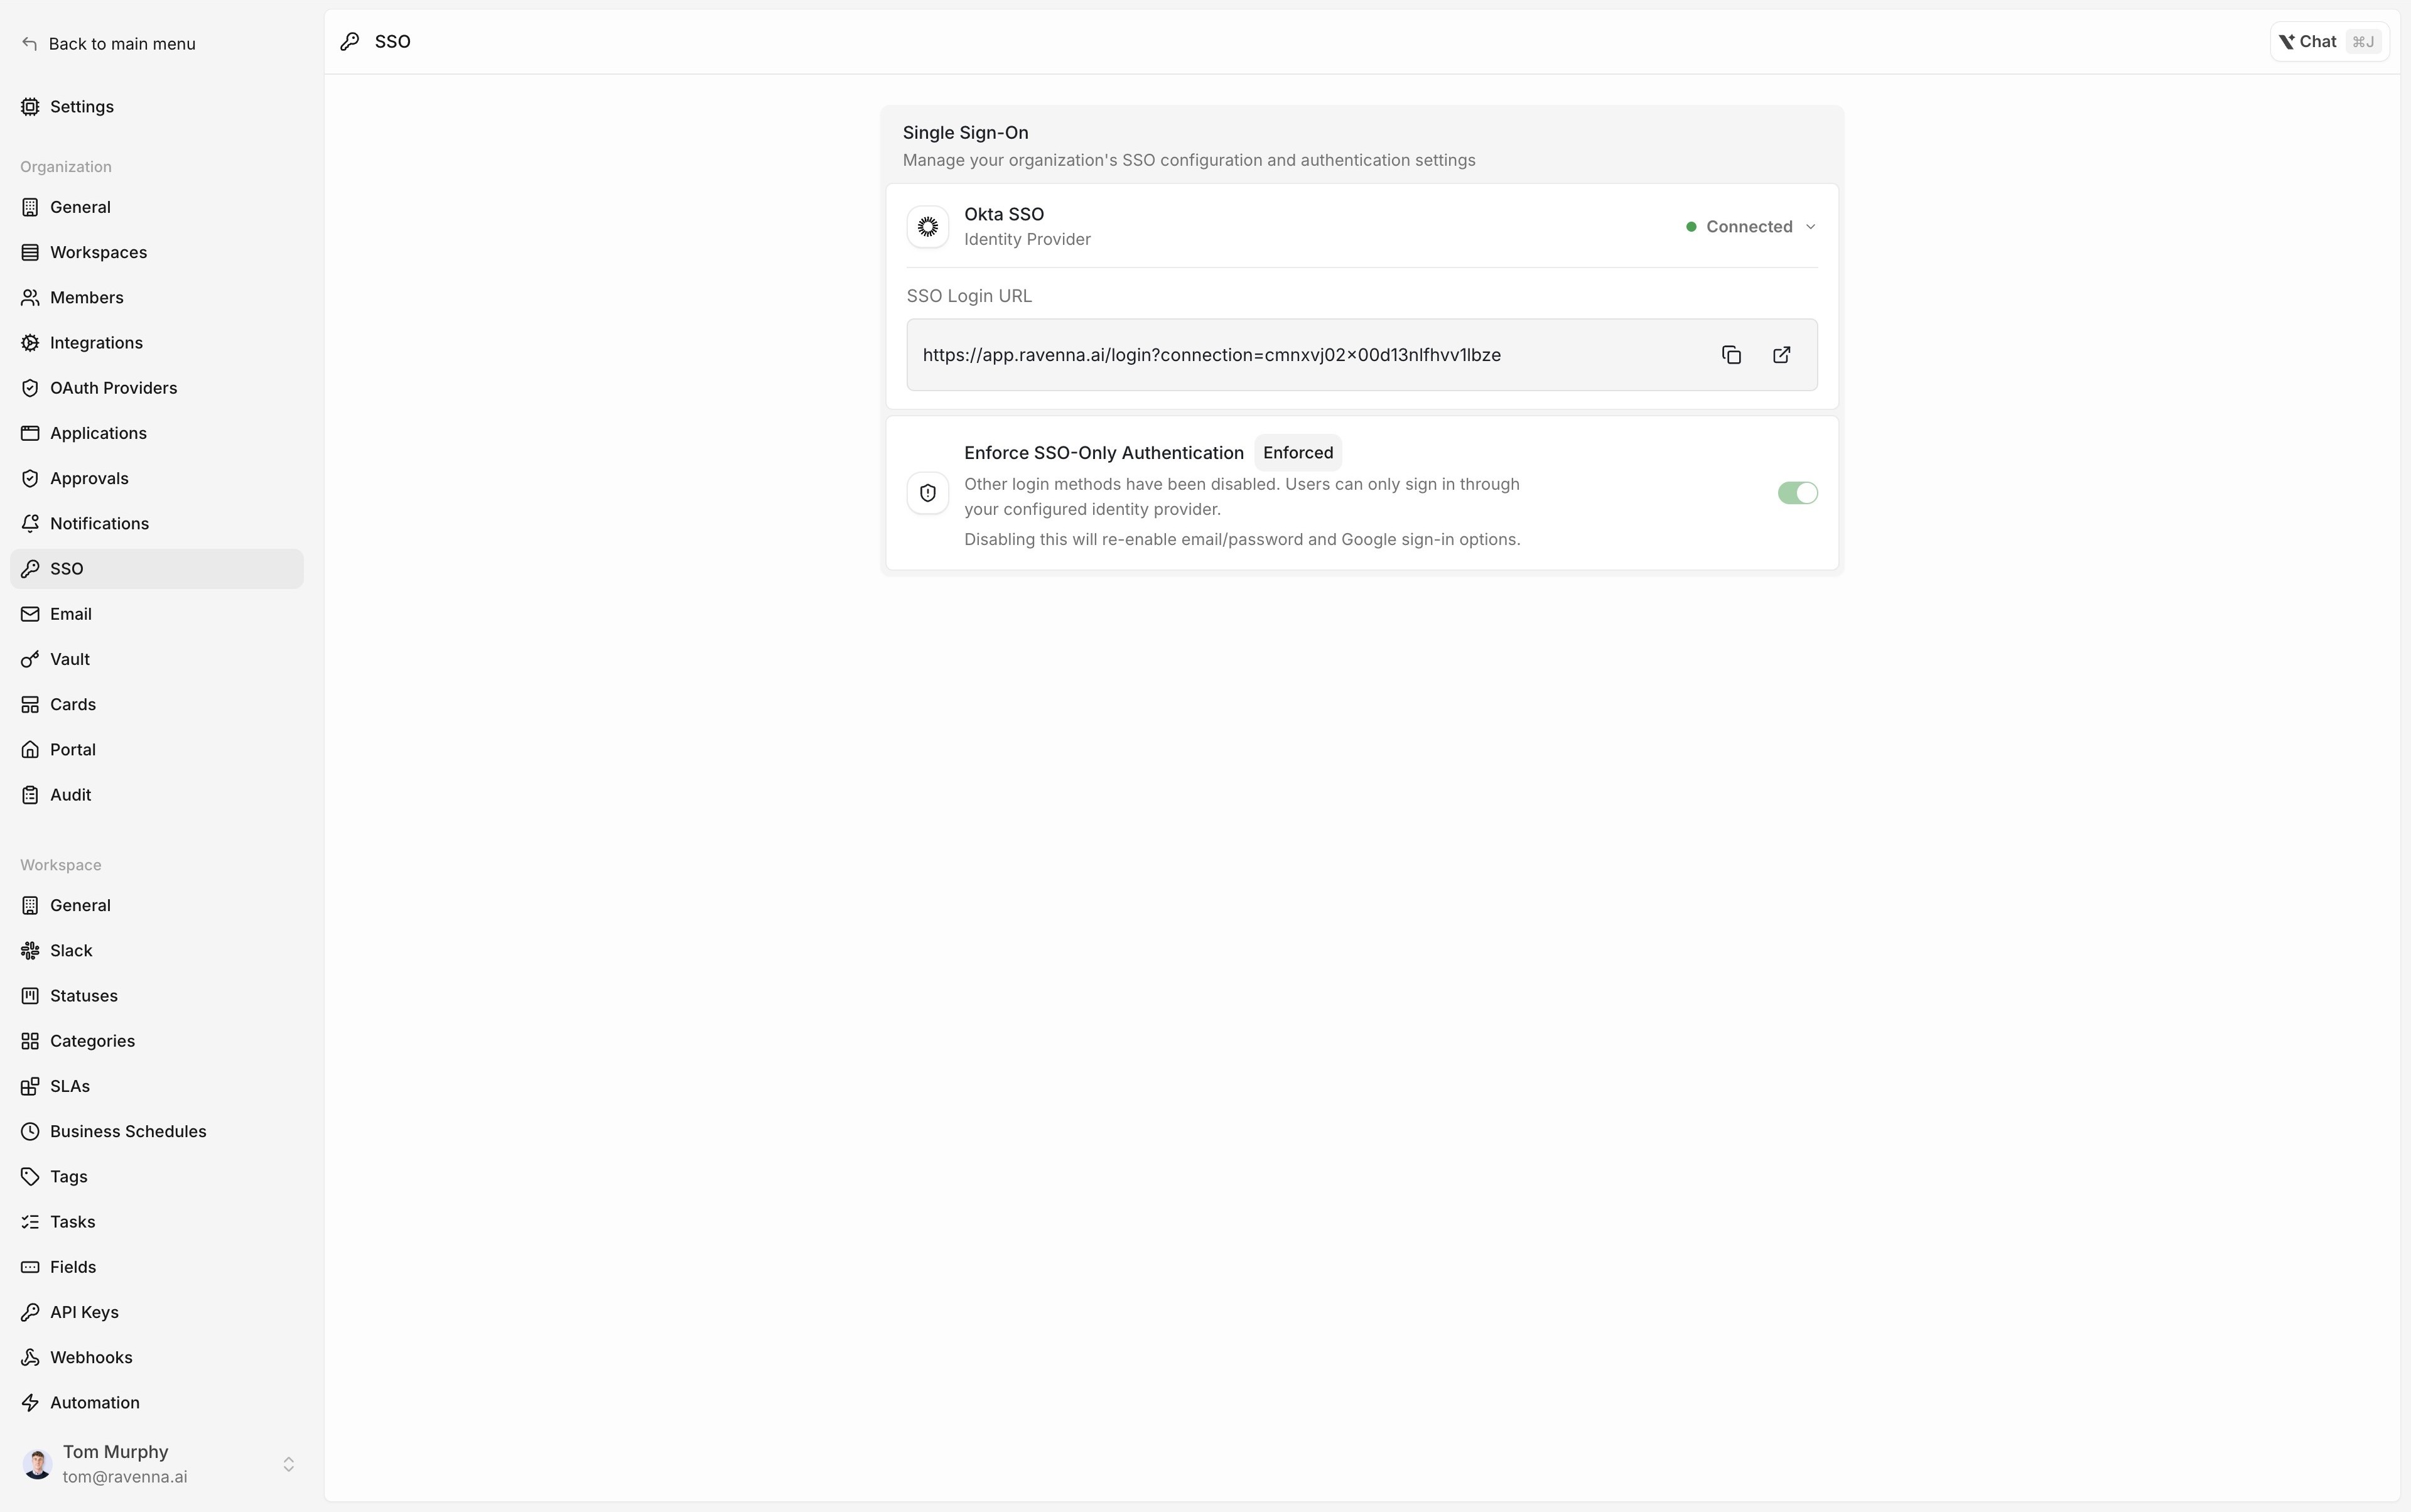
The **Single Sign-On** card on **Settings > SSO** shows your connection and its status.
| Status | What it means |
| - | - |
| Connected | SSO is on. The card shows your **SSO Login URL** and the **Enforce SSO-Only Authentication** section. |
| Not Connected | The connection is set up but turned off, for example after you disconnect it. Click **Connect** to turn it back on. |
 ## Edit the connection
Edit the connection when your IdP's details change, such as a new signing certificate or client secret, or to change your domains.
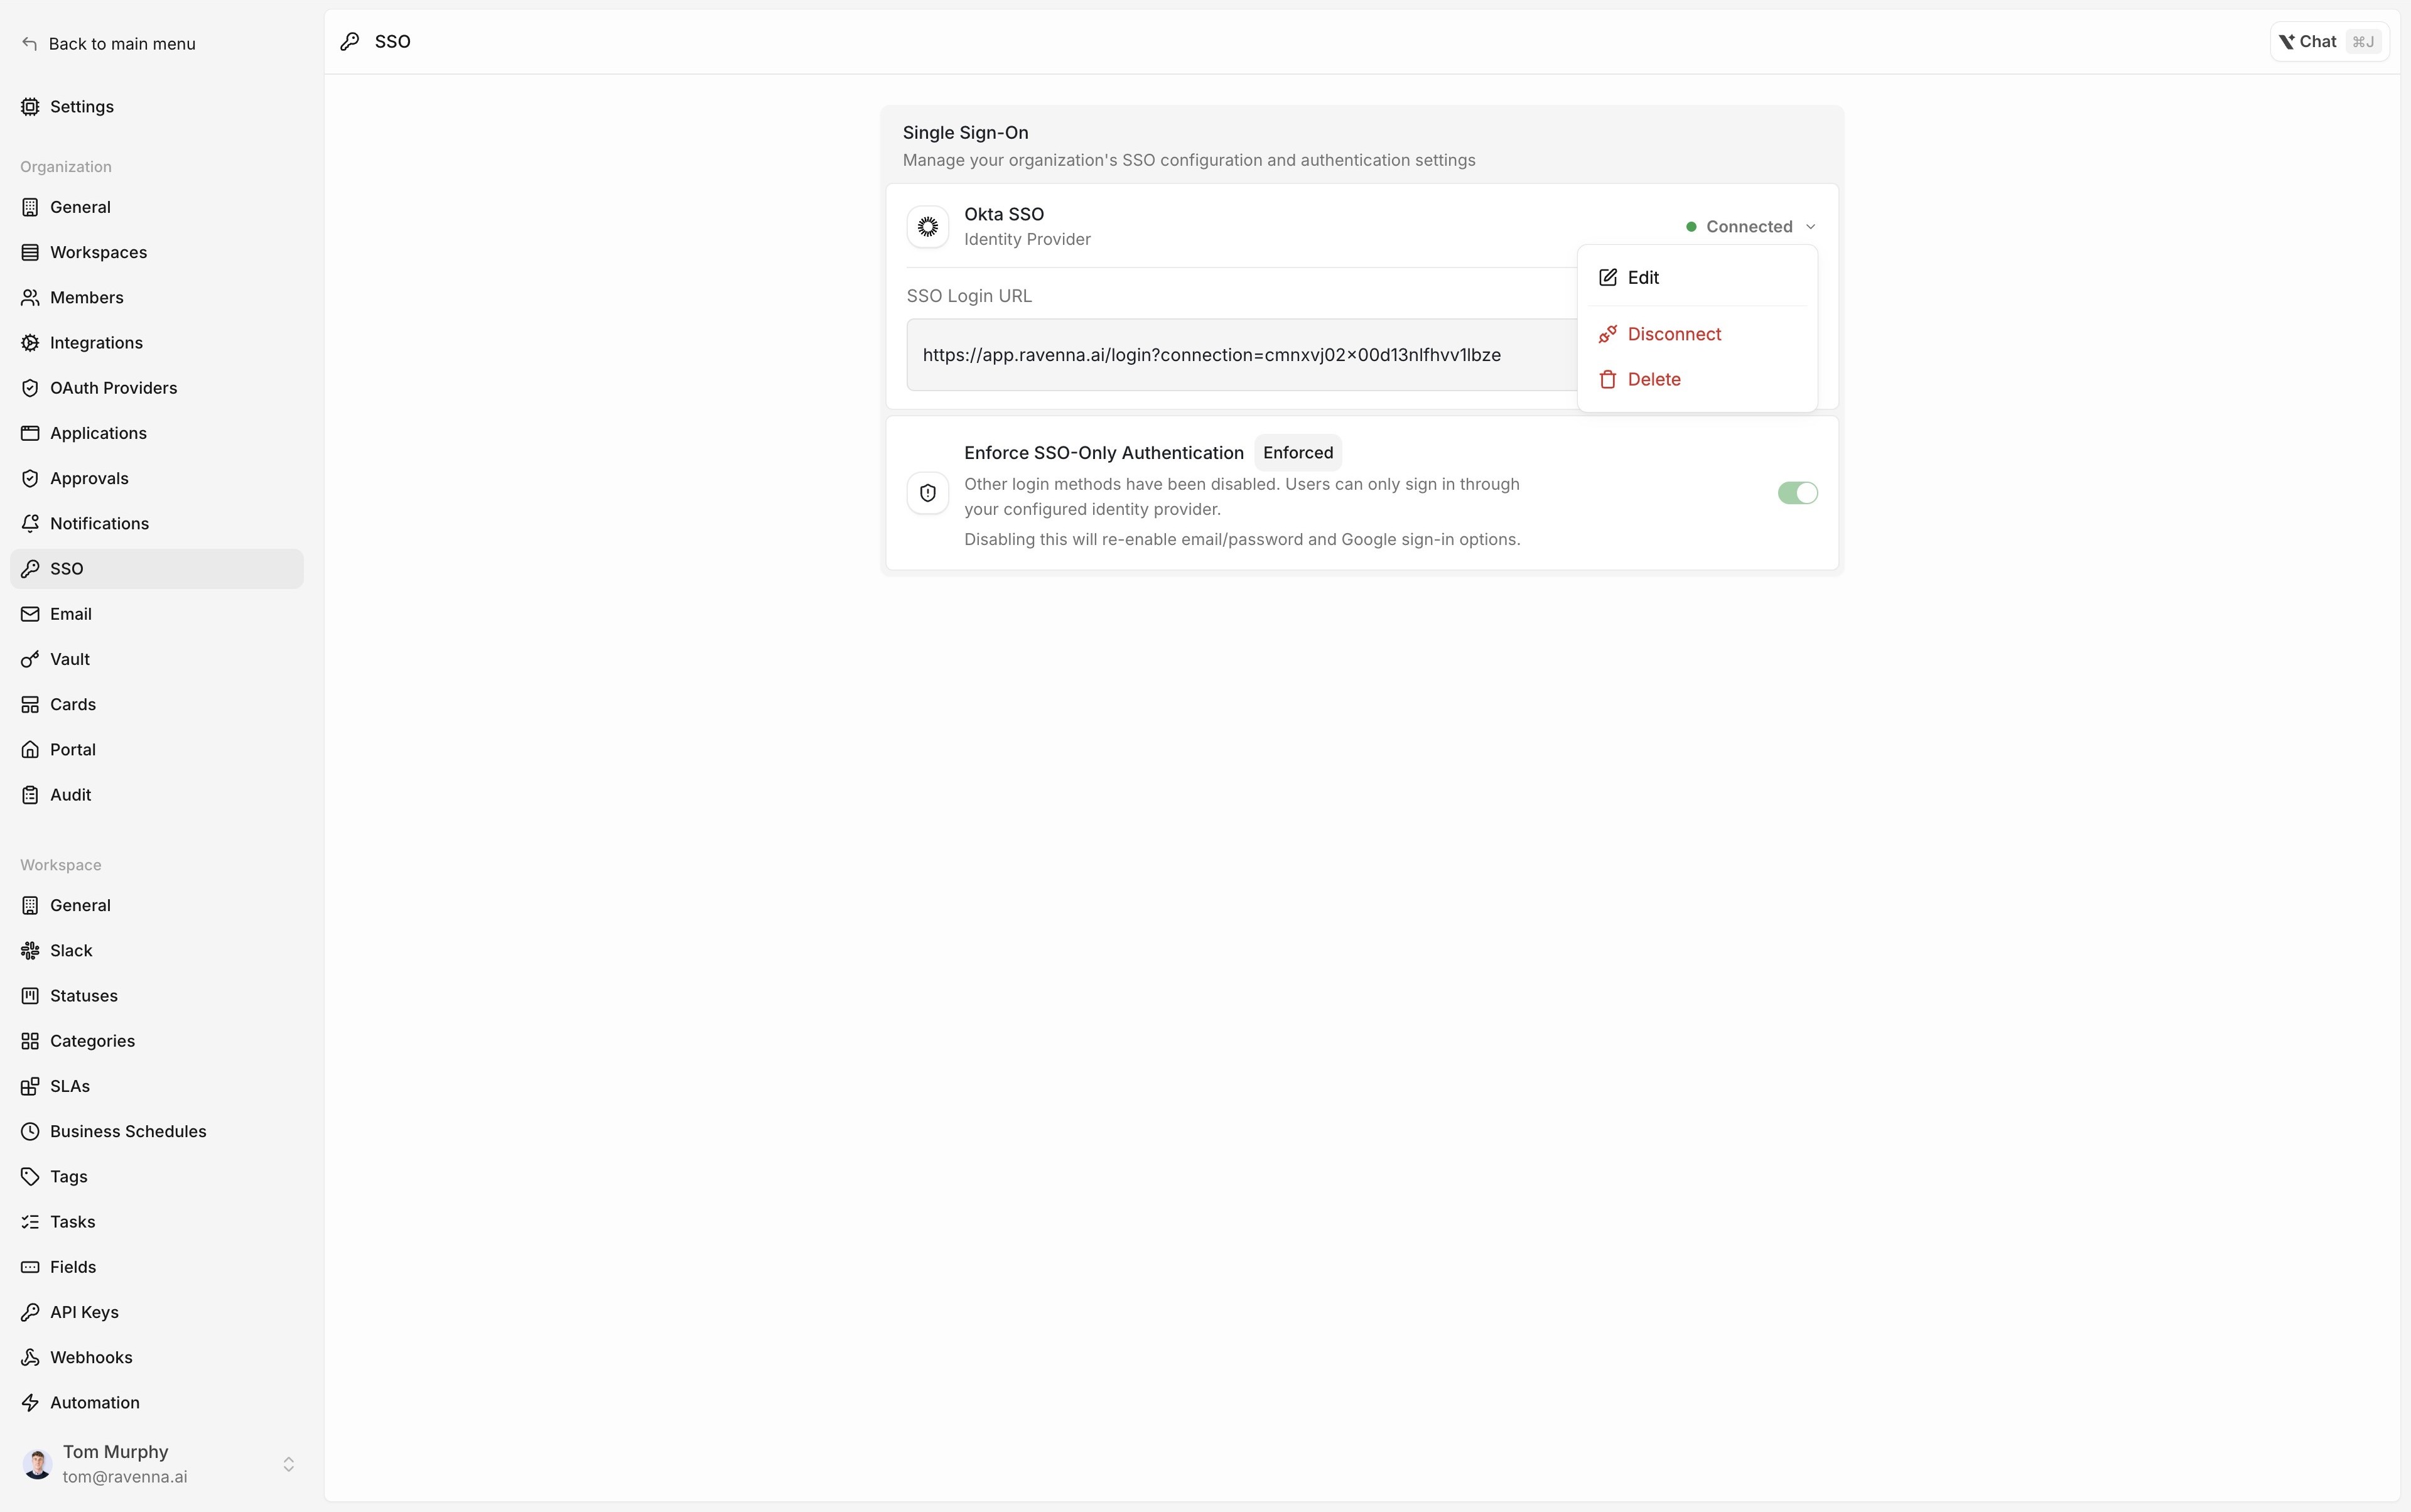
On **Settings > SSO**, click the **Connected** dropdown and select **Edit**.
 The setup wizard opens in a new tab. Update the connection details or domains the same way you entered them during [setup](/integrations/sso/setup#configure-your-identity-provider).
Click **Test Connection** to confirm users can still sign in, then click **Done**.
### Replace an expiring SAML certificate
SAML providers sign each sign-in with a certificate that expires. If it expires before you replace it, no one can sign in until you update it. OIDC connections don't use a certificate you manage.
Create the new signing certificate for the Ravenna application before the current one expires.
[Edit the connection](#edit-the-connection) and replace the old certificate with the new one.
Click **Test Connection** in the wizard, then click **Done**.
## Enforce SSO-only sign-in
Ravenna doesn't turn on other sign-in methods by default, so for most organizations **Enforce SSO-Only Authentication** already shows **Enforced** and there's nothing to do.
If your organization has other sign-in methods turned on, such as email and password or Google, the section says so and the switch is available. Turning it on turns those methods off for everyone in your organization.
You can't turn enforcement off. To let users sign in another way again, [disconnect SSO](#disconnect-or-delete-the-connection). If your organization needs a specific sign-in method, such as email and password, contact [Ravenna support](mailto:support@ravenna.ai).
On **Settings > SSO**, in **Enforce SSO-Only Authentication**, turn on the switch.
Click **Disable Other Methods**. An **Enforced** badge appears next to the section title.
## Disconnect or delete the connection
Turns SSO off and keeps its configuration. Your organization goes back to Ravenna's default sign-in methods. Click **Connect** to turn it back on.
Removes the connection and its configuration. Other sign-in methods stay off.
Deleting the connection doesn't turn other sign-in methods back on. Disconnect before you delete, or your users may have no way to sign in.
On **Settings > SSO**, click the **Connected** dropdown and select **Disconnect** or **Delete**.
Type the connection name shown in the dialog, such as **Okta SSO**, then confirm.
## Monitor sign-in activity
Use your IdP's sign-in logs to see who signed in to Ravenna and why a sign-in failed, such as the System Log in Okta or the sign-in logs in Microsoft Entra ID.
Ravenna's [audit log](/documentation/platform/organizations/audit-log) doesn't record SSO sign-ins or changes to the SSO connection.
Learn more about [reviewing user access](/integrations/sso/user-management#review-user-access)
## Related topics
- [User management](/integrations/sso/user-management.md)
- [Setup](/integrations/sso/setup.md)
- [Organization settings](/documentation/platform/organizations/settings.md)
- [Troubleshooting](/integrations/sso/troubleshooting.md)
- [Workflows](/integrations/microsoft-entra/workflows.md)
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.