

Check the connection status
The Single Sign-On card on Settings > SSO shows your connection and its status.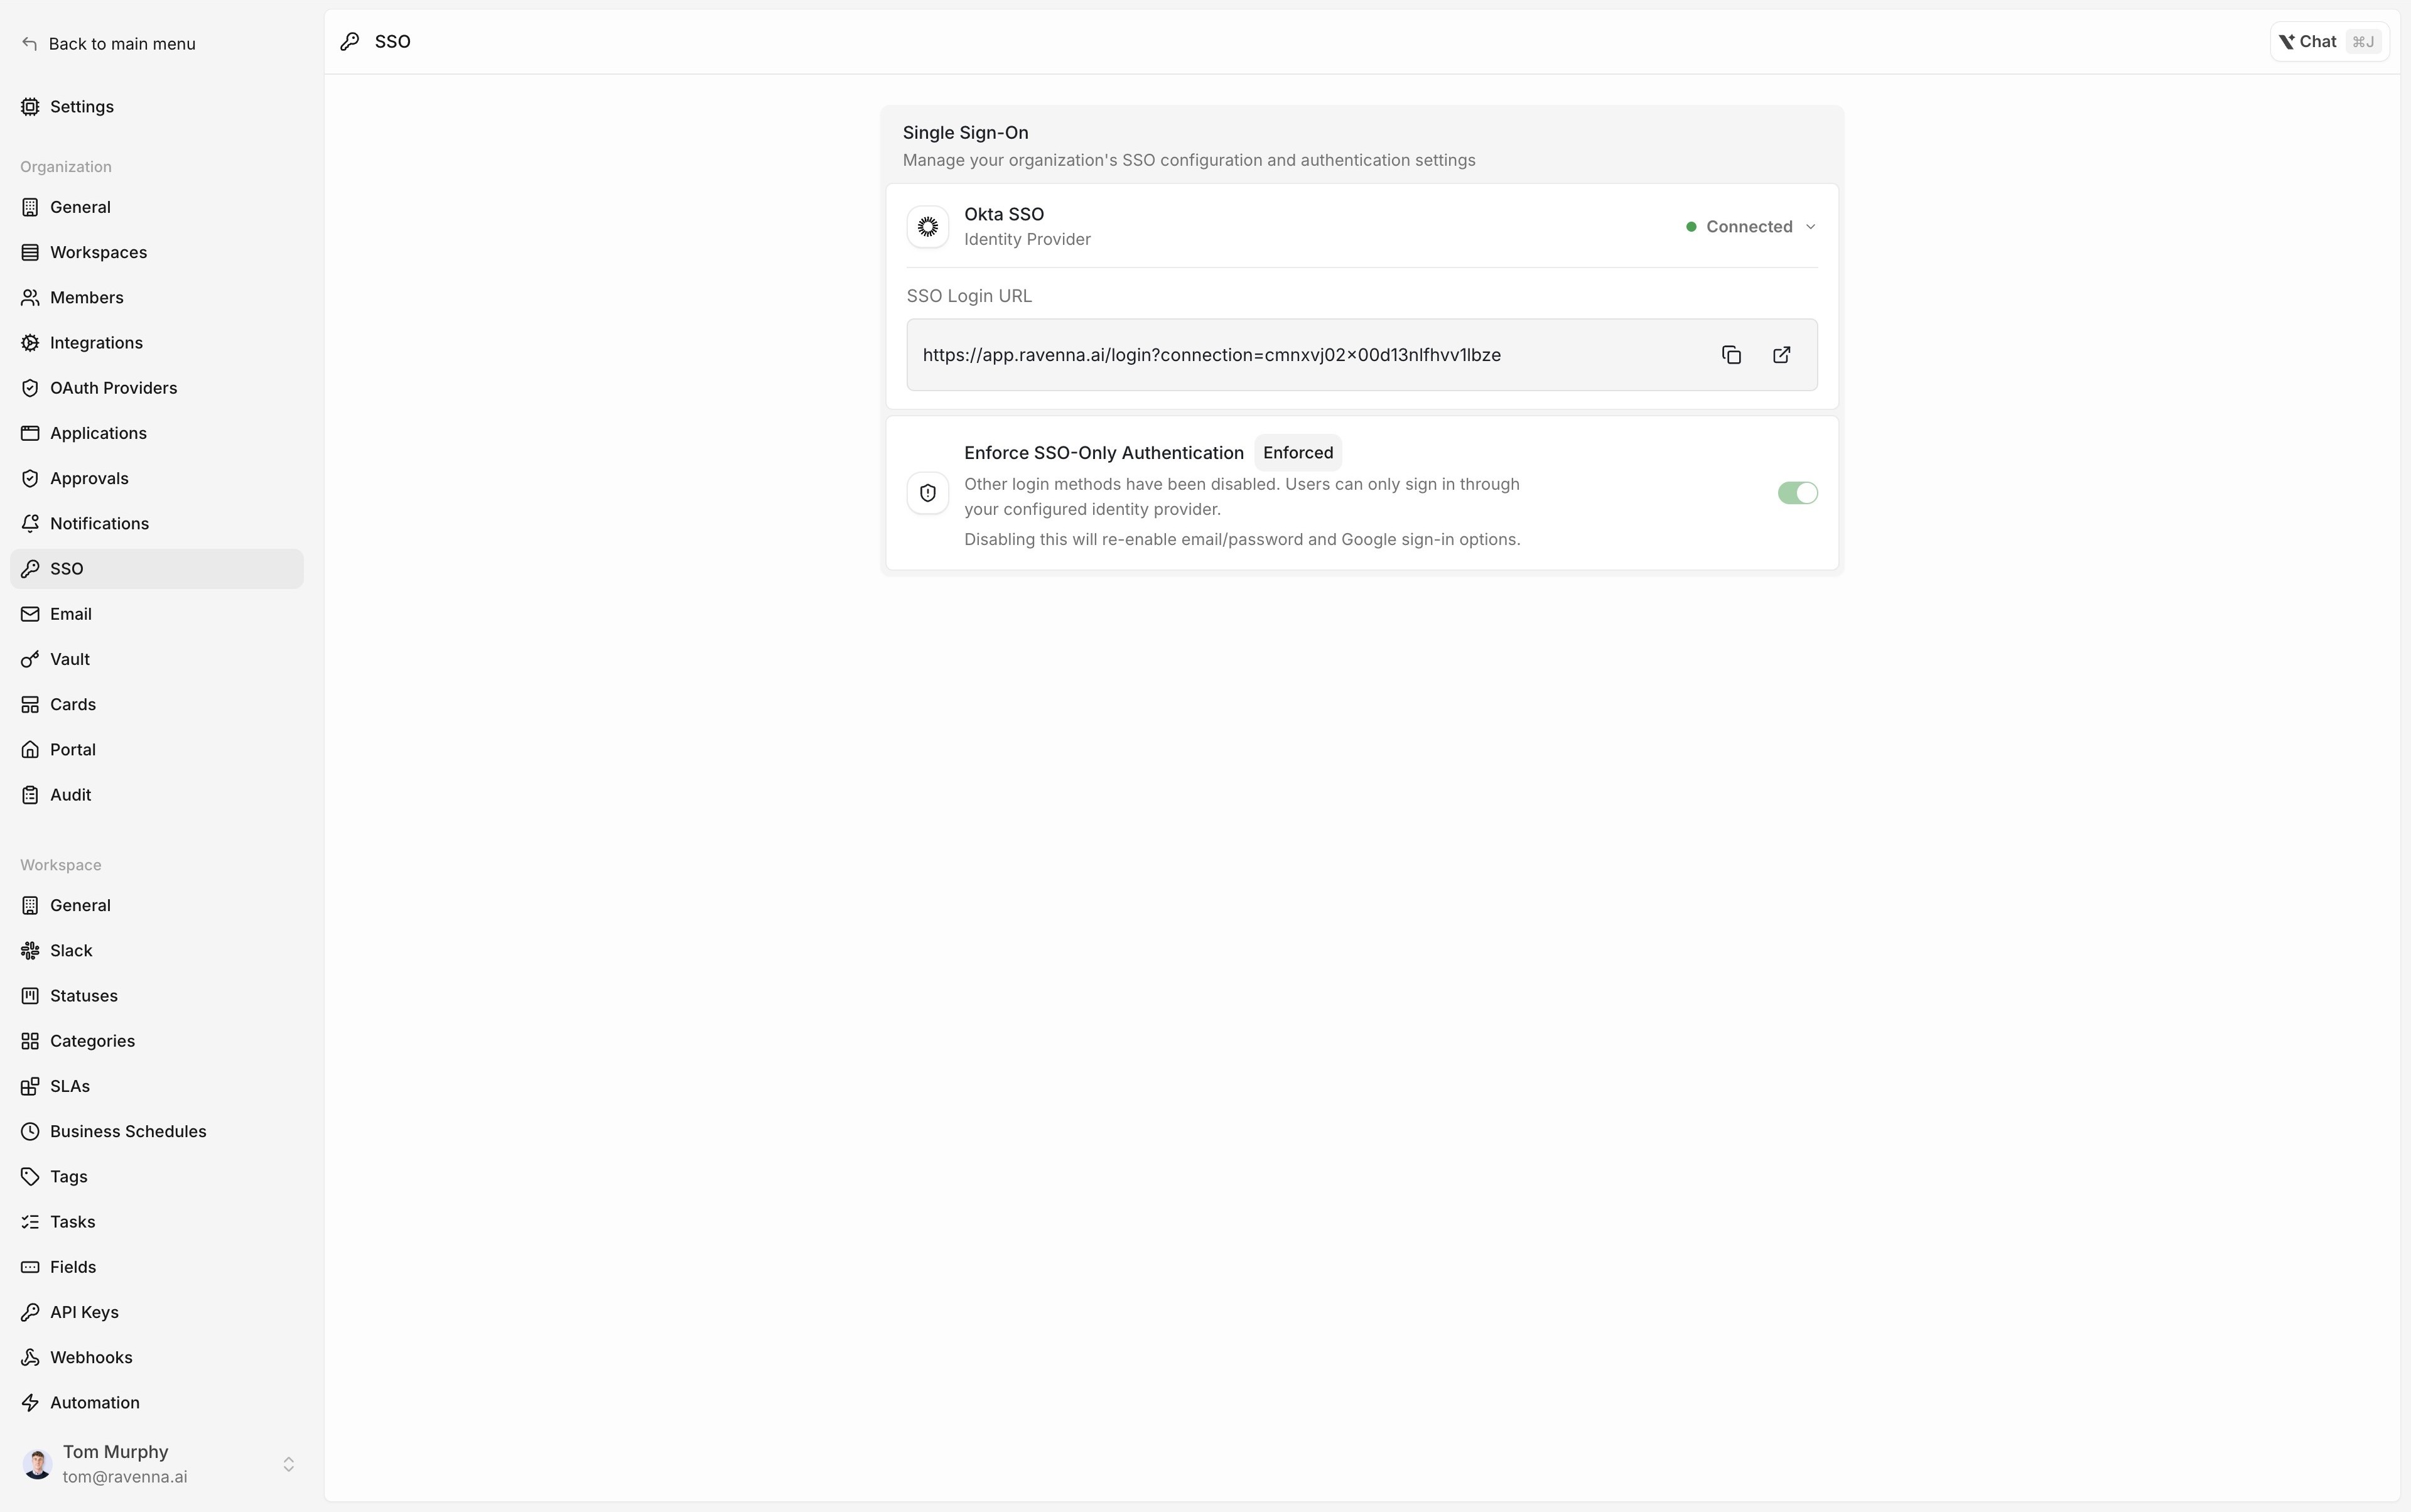
Edit the connection
Edit the connection when your IdP’s details change, such as a new signing certificate or client secret, or to change your domains.1
Open the connection menu
On Settings > SSO, click the Connected dropdown and select Edit.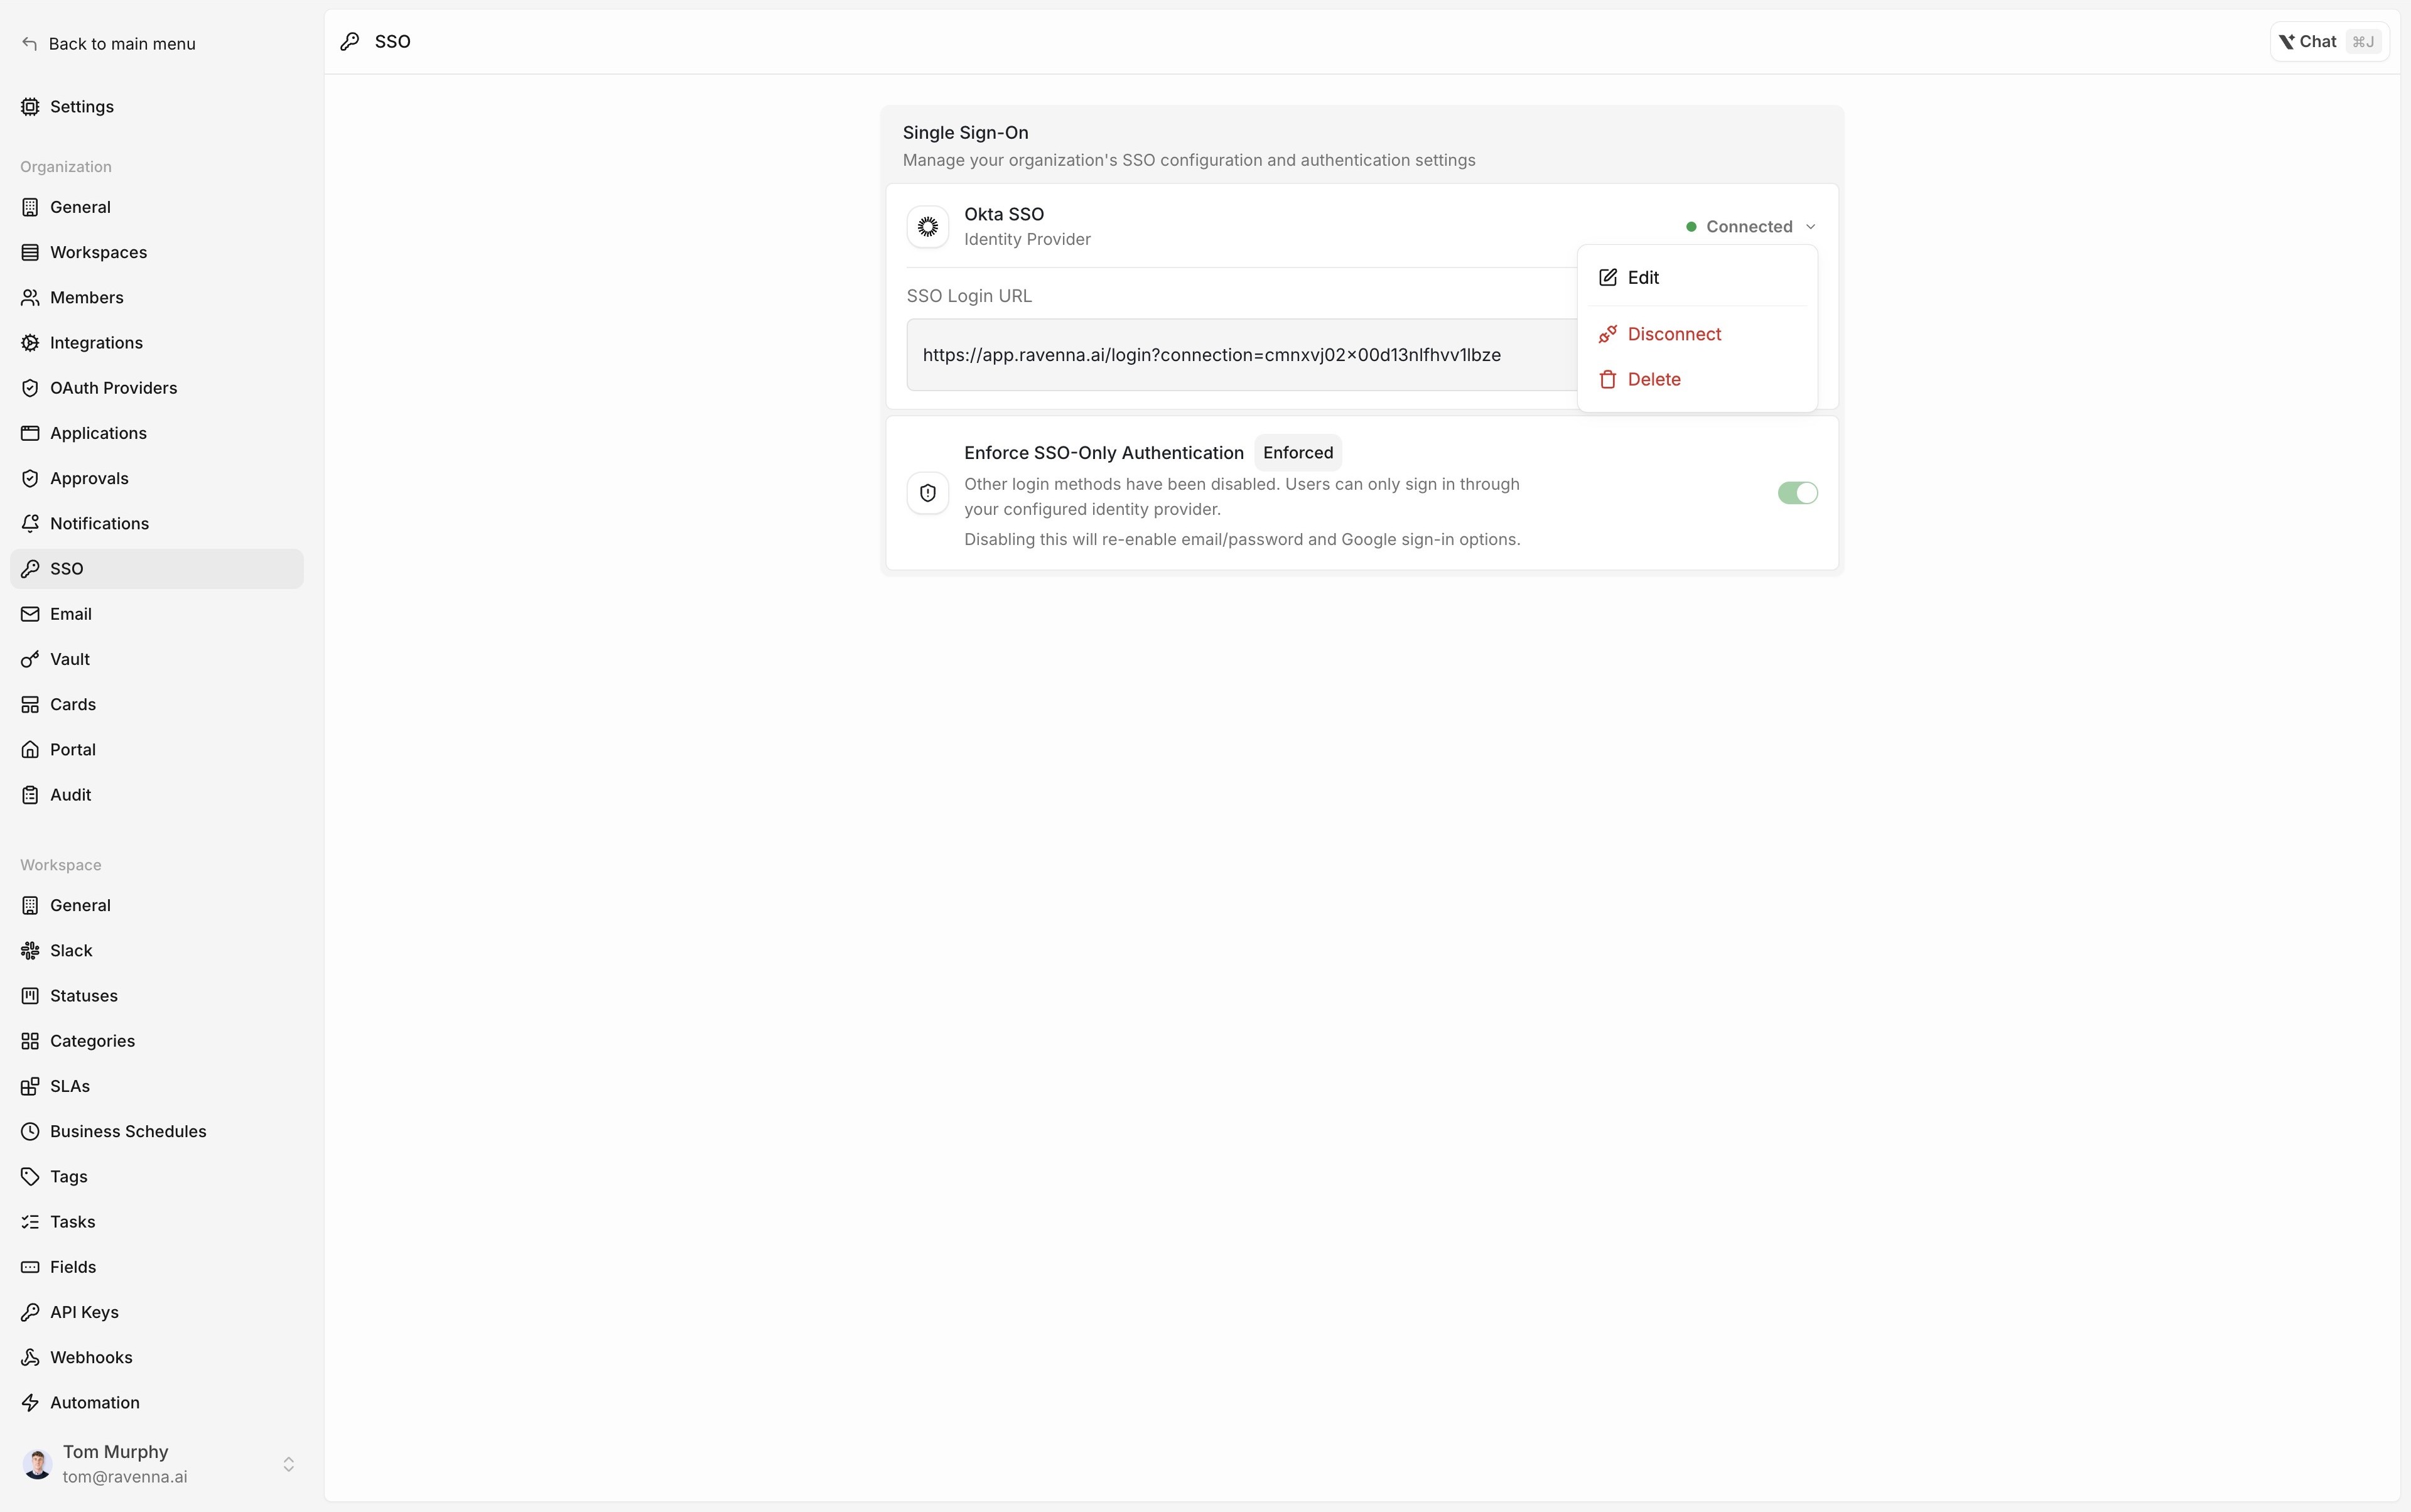
2
Update the details in the wizard
The setup wizard opens in a new tab. Update the connection details or domains the same way you entered them during setup.
3
Test the connection
Click Test Connection to confirm users can still sign in, then click Done.
Replace an expiring SAML certificate
SAML providers sign each sign-in with a certificate that expires. If it expires before you replace it, no one can sign in until you update it. OIDC connections don’t use a certificate you manage.1
Generate a new certificate in your IdP
Create the new signing certificate for the Ravenna application before the current one expires.
2
Replace it in Ravenna
Edit the connection and replace the old certificate with the new one.
3
Test the connection
Click Test Connection in the wizard, then click Done.
Enforce SSO-only sign-in
Ravenna doesn’t turn on other sign-in methods by default, so for most organizations Enforce SSO-Only Authentication already shows Enforced and there’s nothing to do.
1
Turn on enforcement
On Settings > SSO, in Enforce SSO-Only Authentication, turn on the switch.
2
Confirm
Click Disable Other Methods. An Enforced badge appears next to the section title.
Disconnect or delete the connection
Disconnect
Turns SSO off and keeps its configuration. Your organization goes back to Ravenna’s default sign-in methods. Click Connect to turn it back on.
Delete
Removes the connection and its configuration. Other sign-in methods stay off.
1
Open the connection menu
On Settings > SSO, click the Connected dropdown and select Disconnect or Delete.
2
Confirm
Type the connection name shown in the dialog, such as Okta SSO, then confirm.
Monitor sign-in activity
Use your IdP’s sign-in logs to see who signed in to Ravenna and why a sign-in failed, such as the System Log in Okta or the sign-in logs in Microsoft Entra ID.Ravenna’s audit log doesn’t record SSO sign-ins or changes to the SSO connection.
Learn more about reviewing user access