
Prerequisites
- Organization admin access in Ravenna
- Admin access to your IdP
- Optional: a connected integration that syncs user profiles into Ravenna, such as an identity provider or HRIS. With one connected, you can skip the wizard’s claims mapping step.
Start the setup wizard
1
Open SSO settings
Go to Settings > SSO and click Connect. The setup wizard opens in a new tab.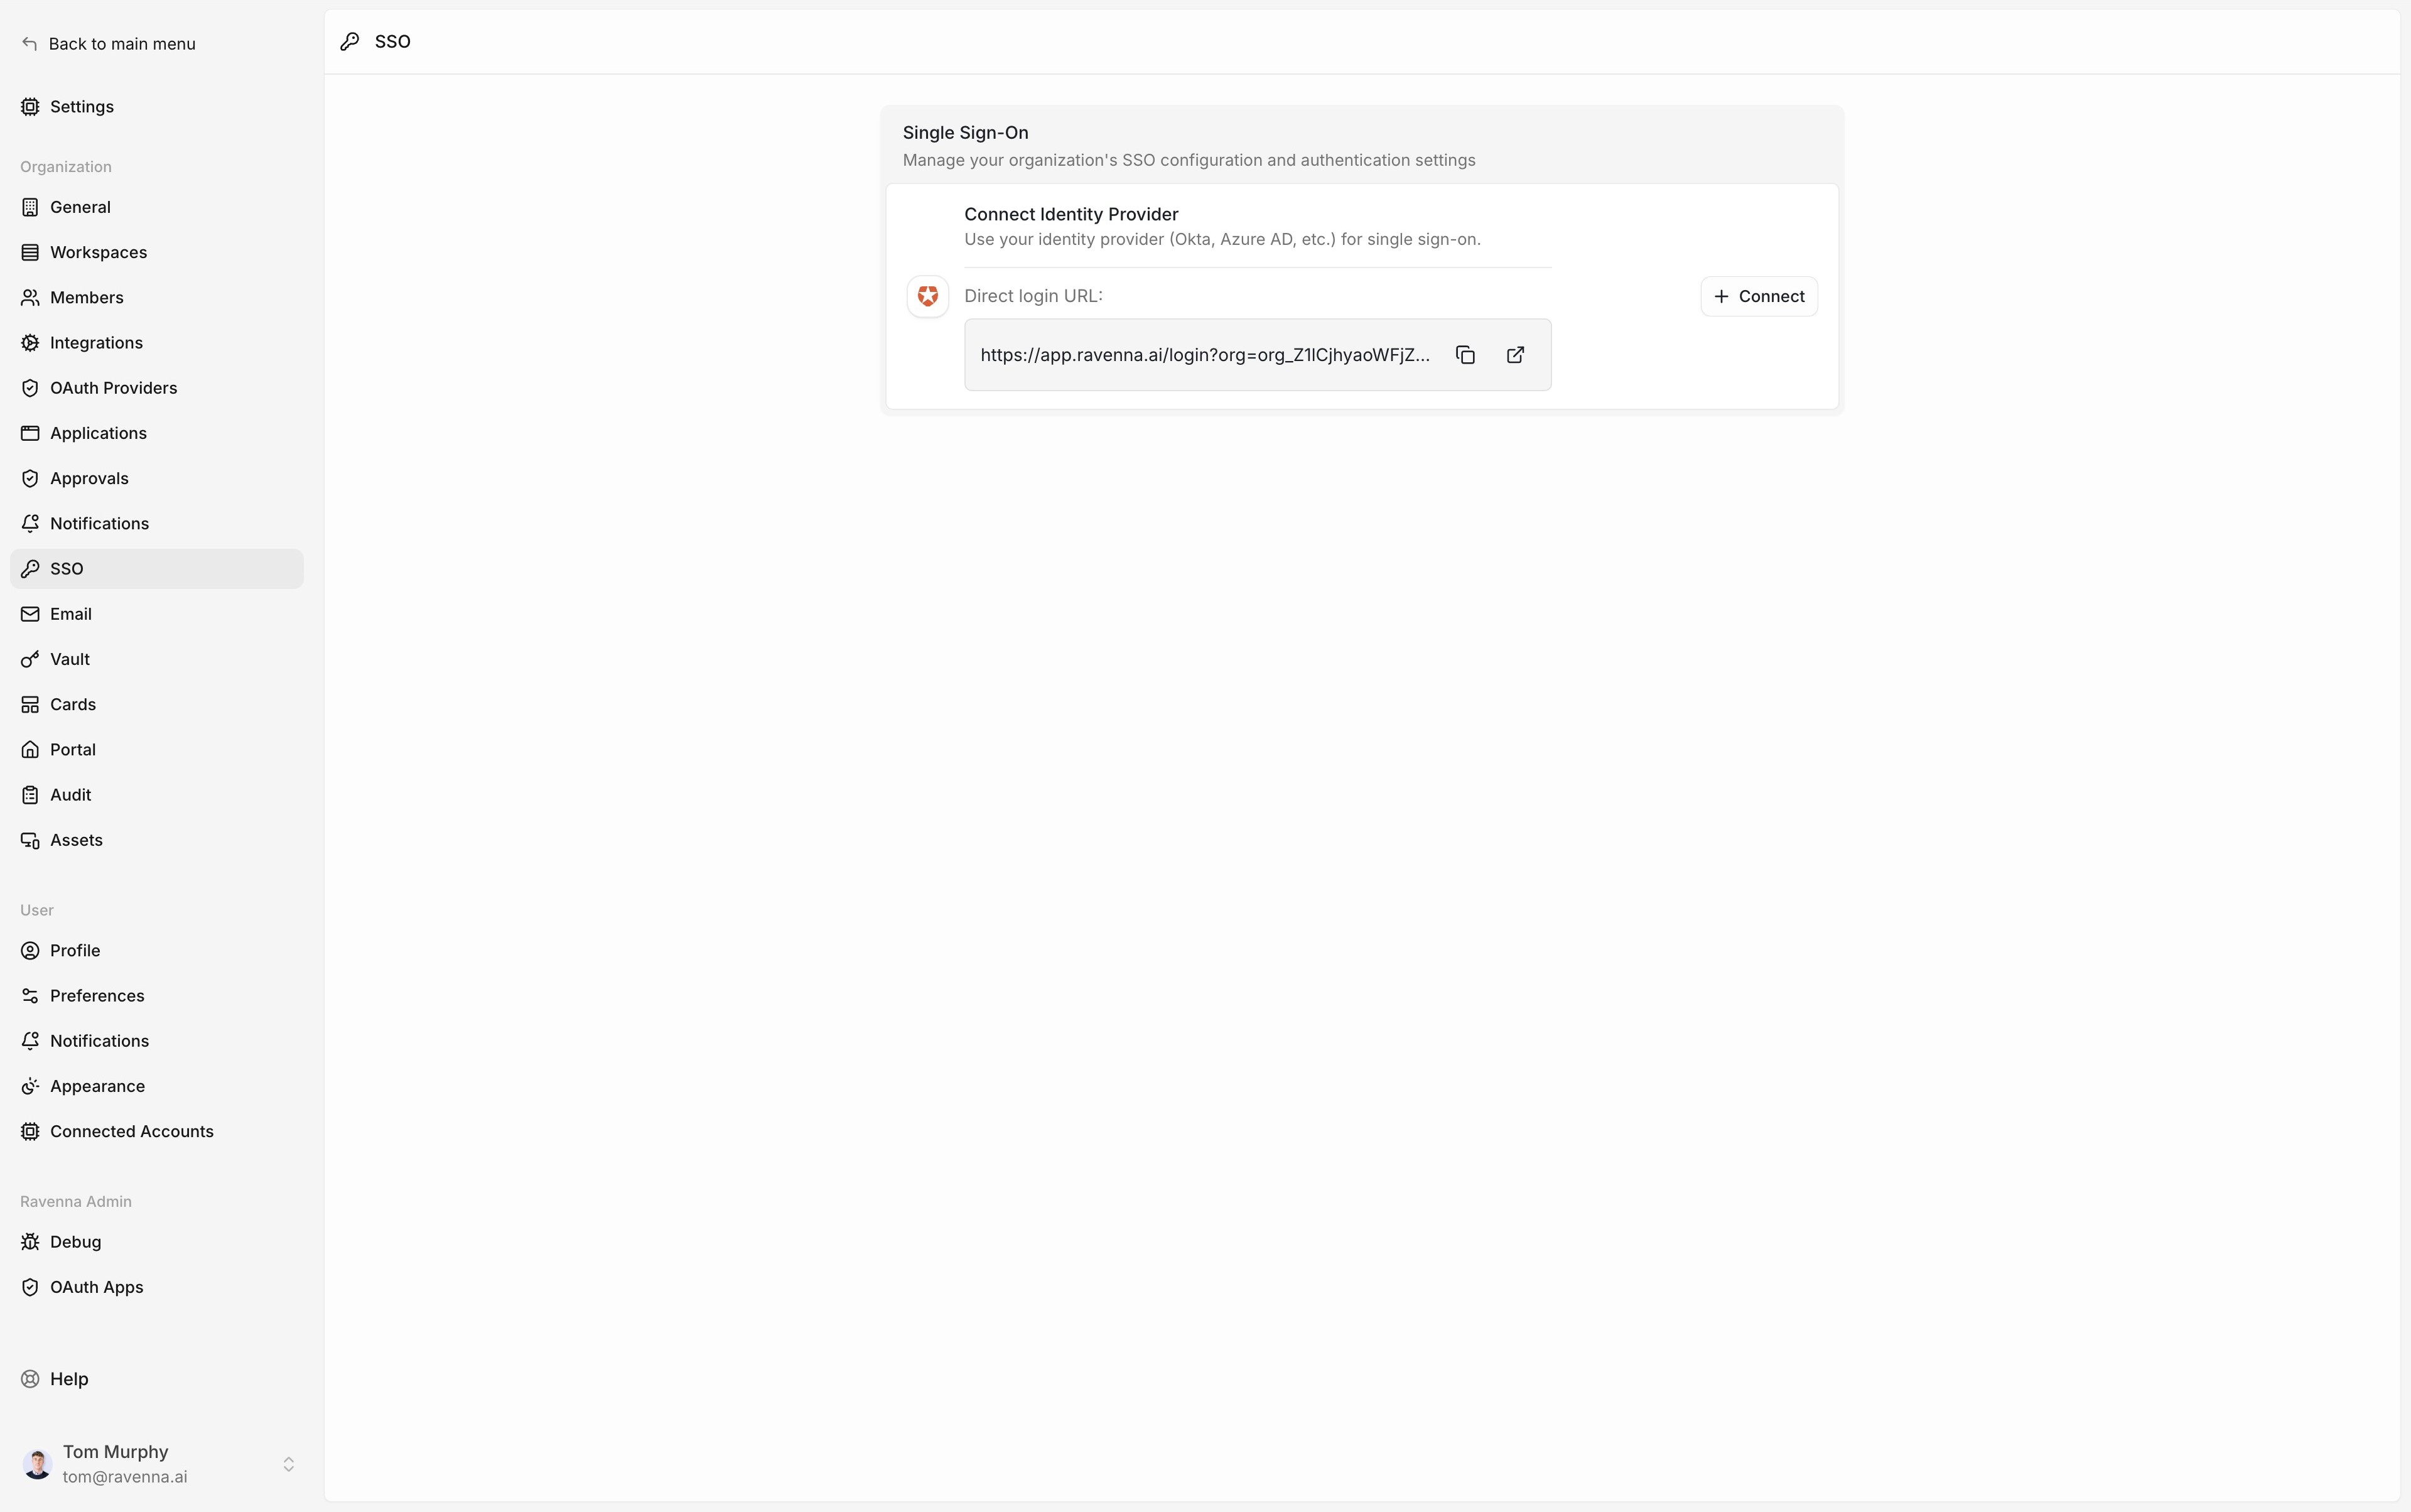
2
Get started
Open your IdP’s admin console in another tab, because you switch between the two. Then click Get Started in the bottom right of the wizard.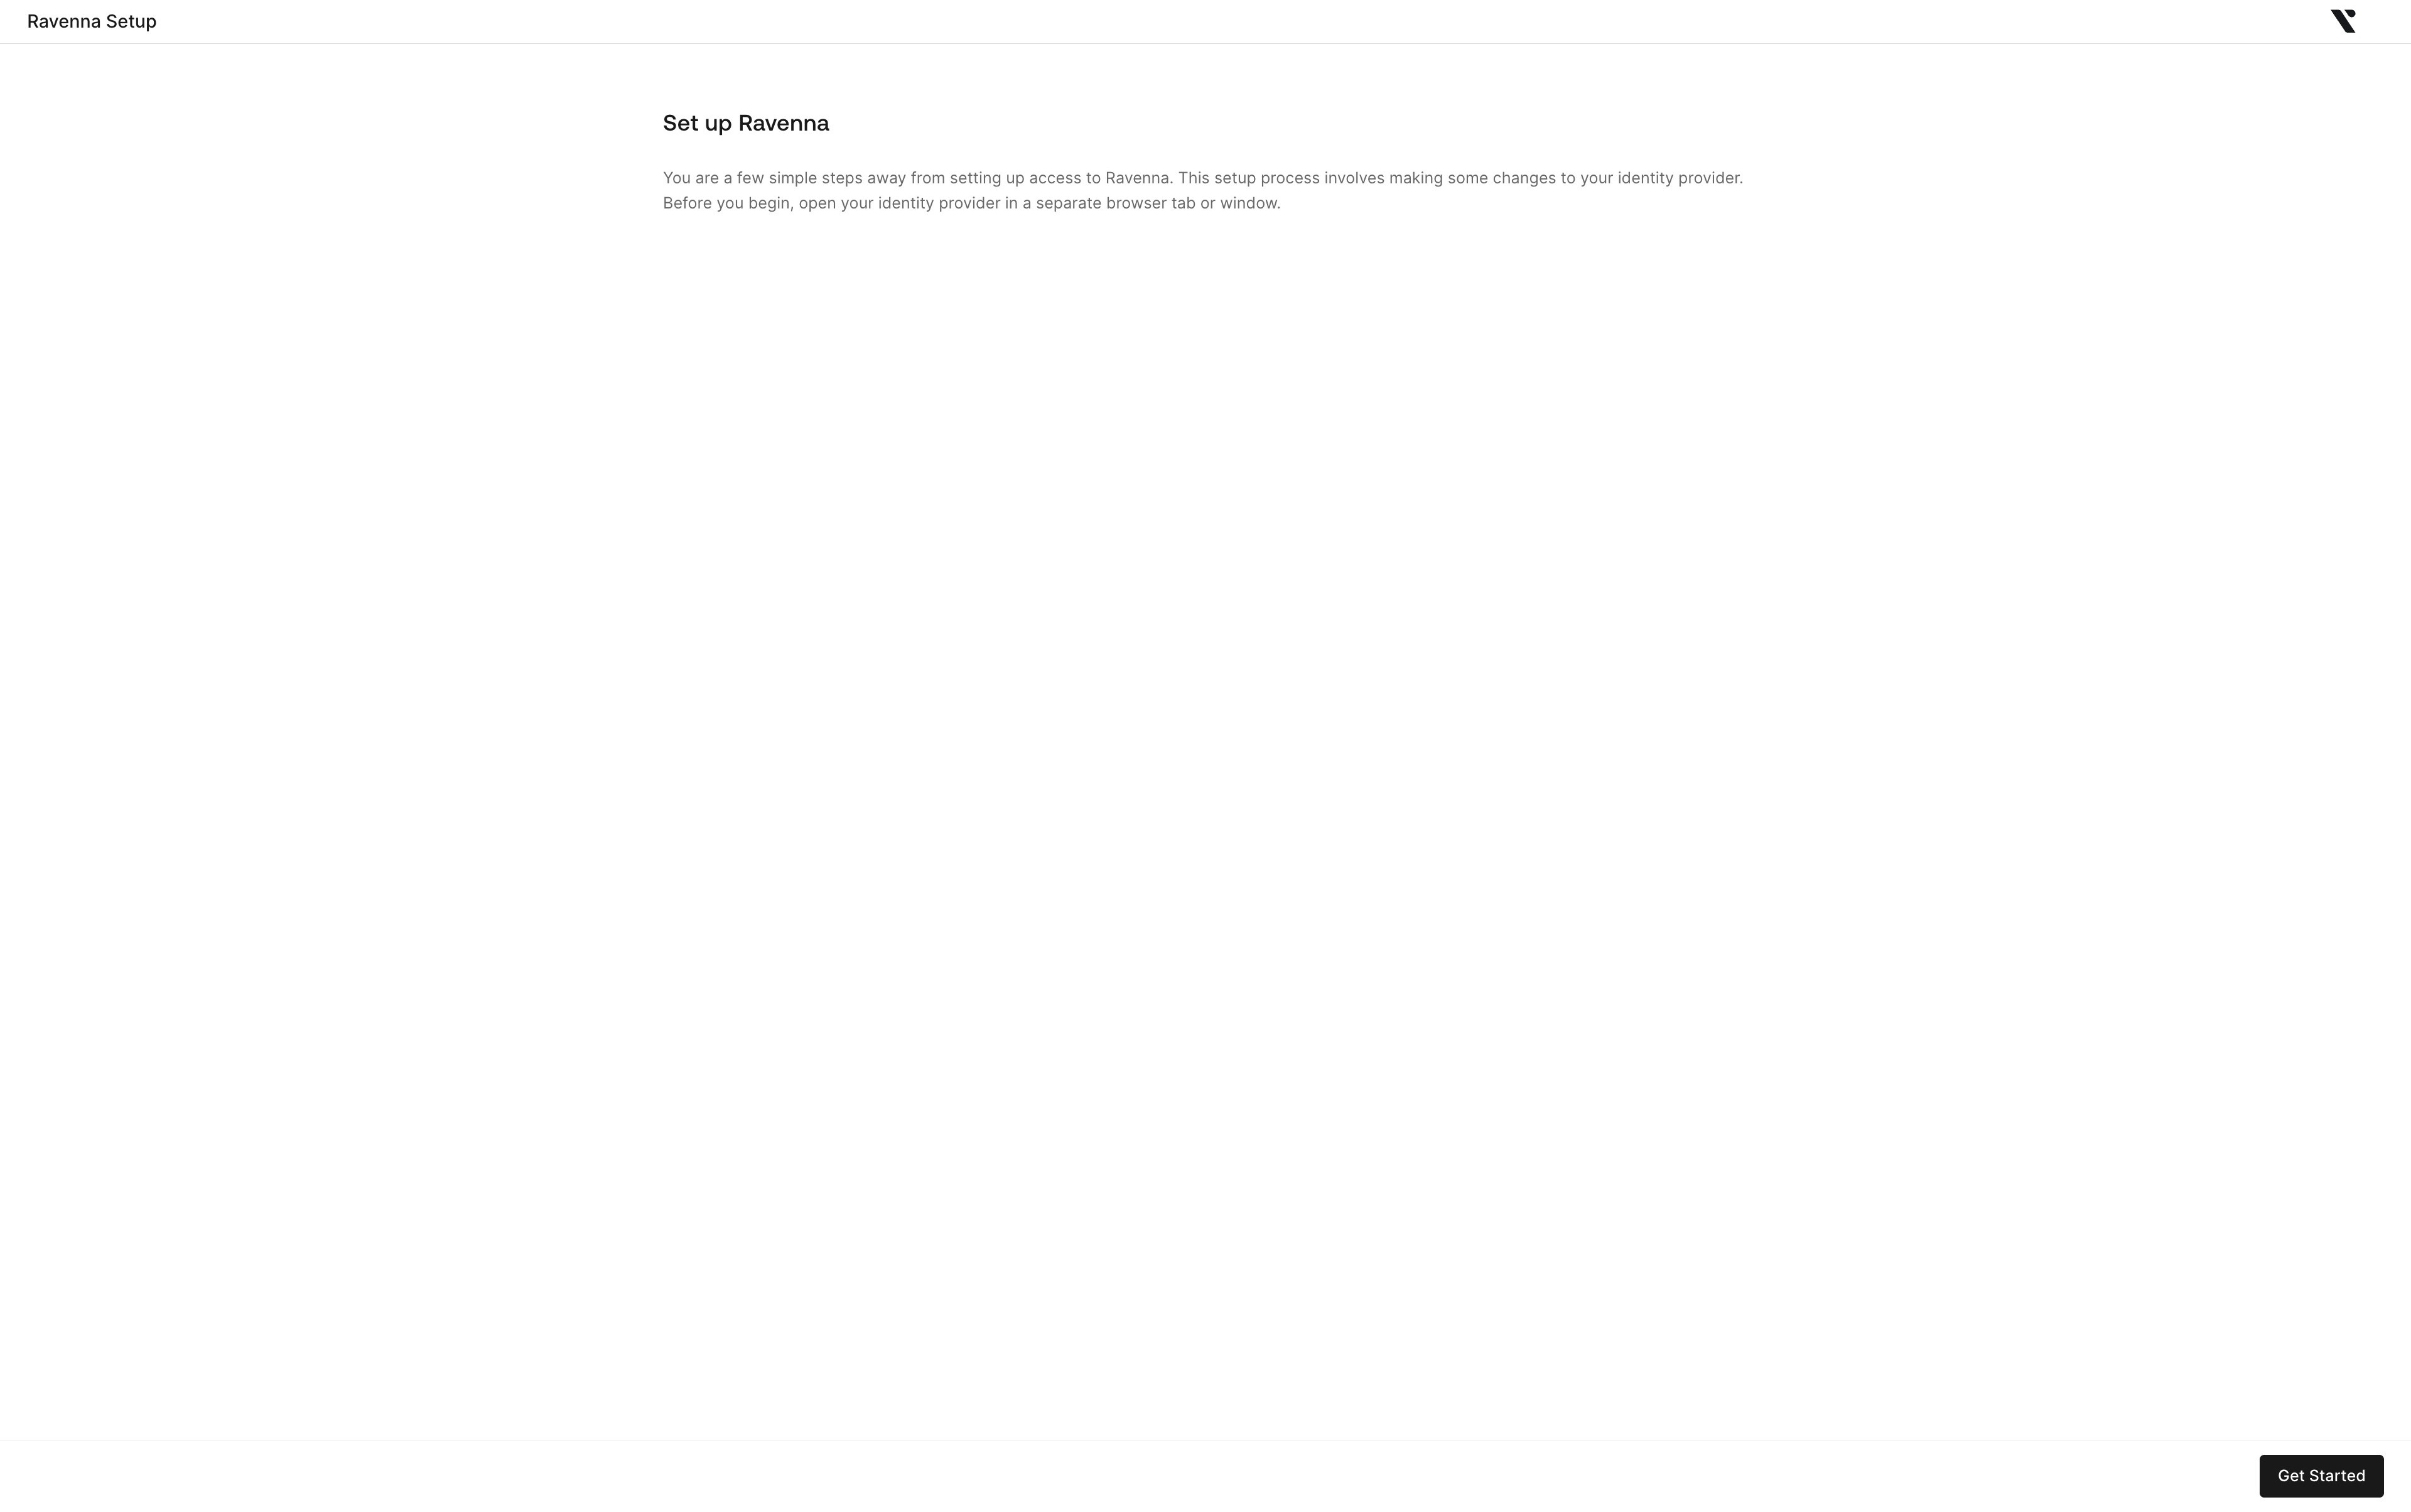
3
Select Single Sign-On
On Configure Your Connection, select Single Sign-On.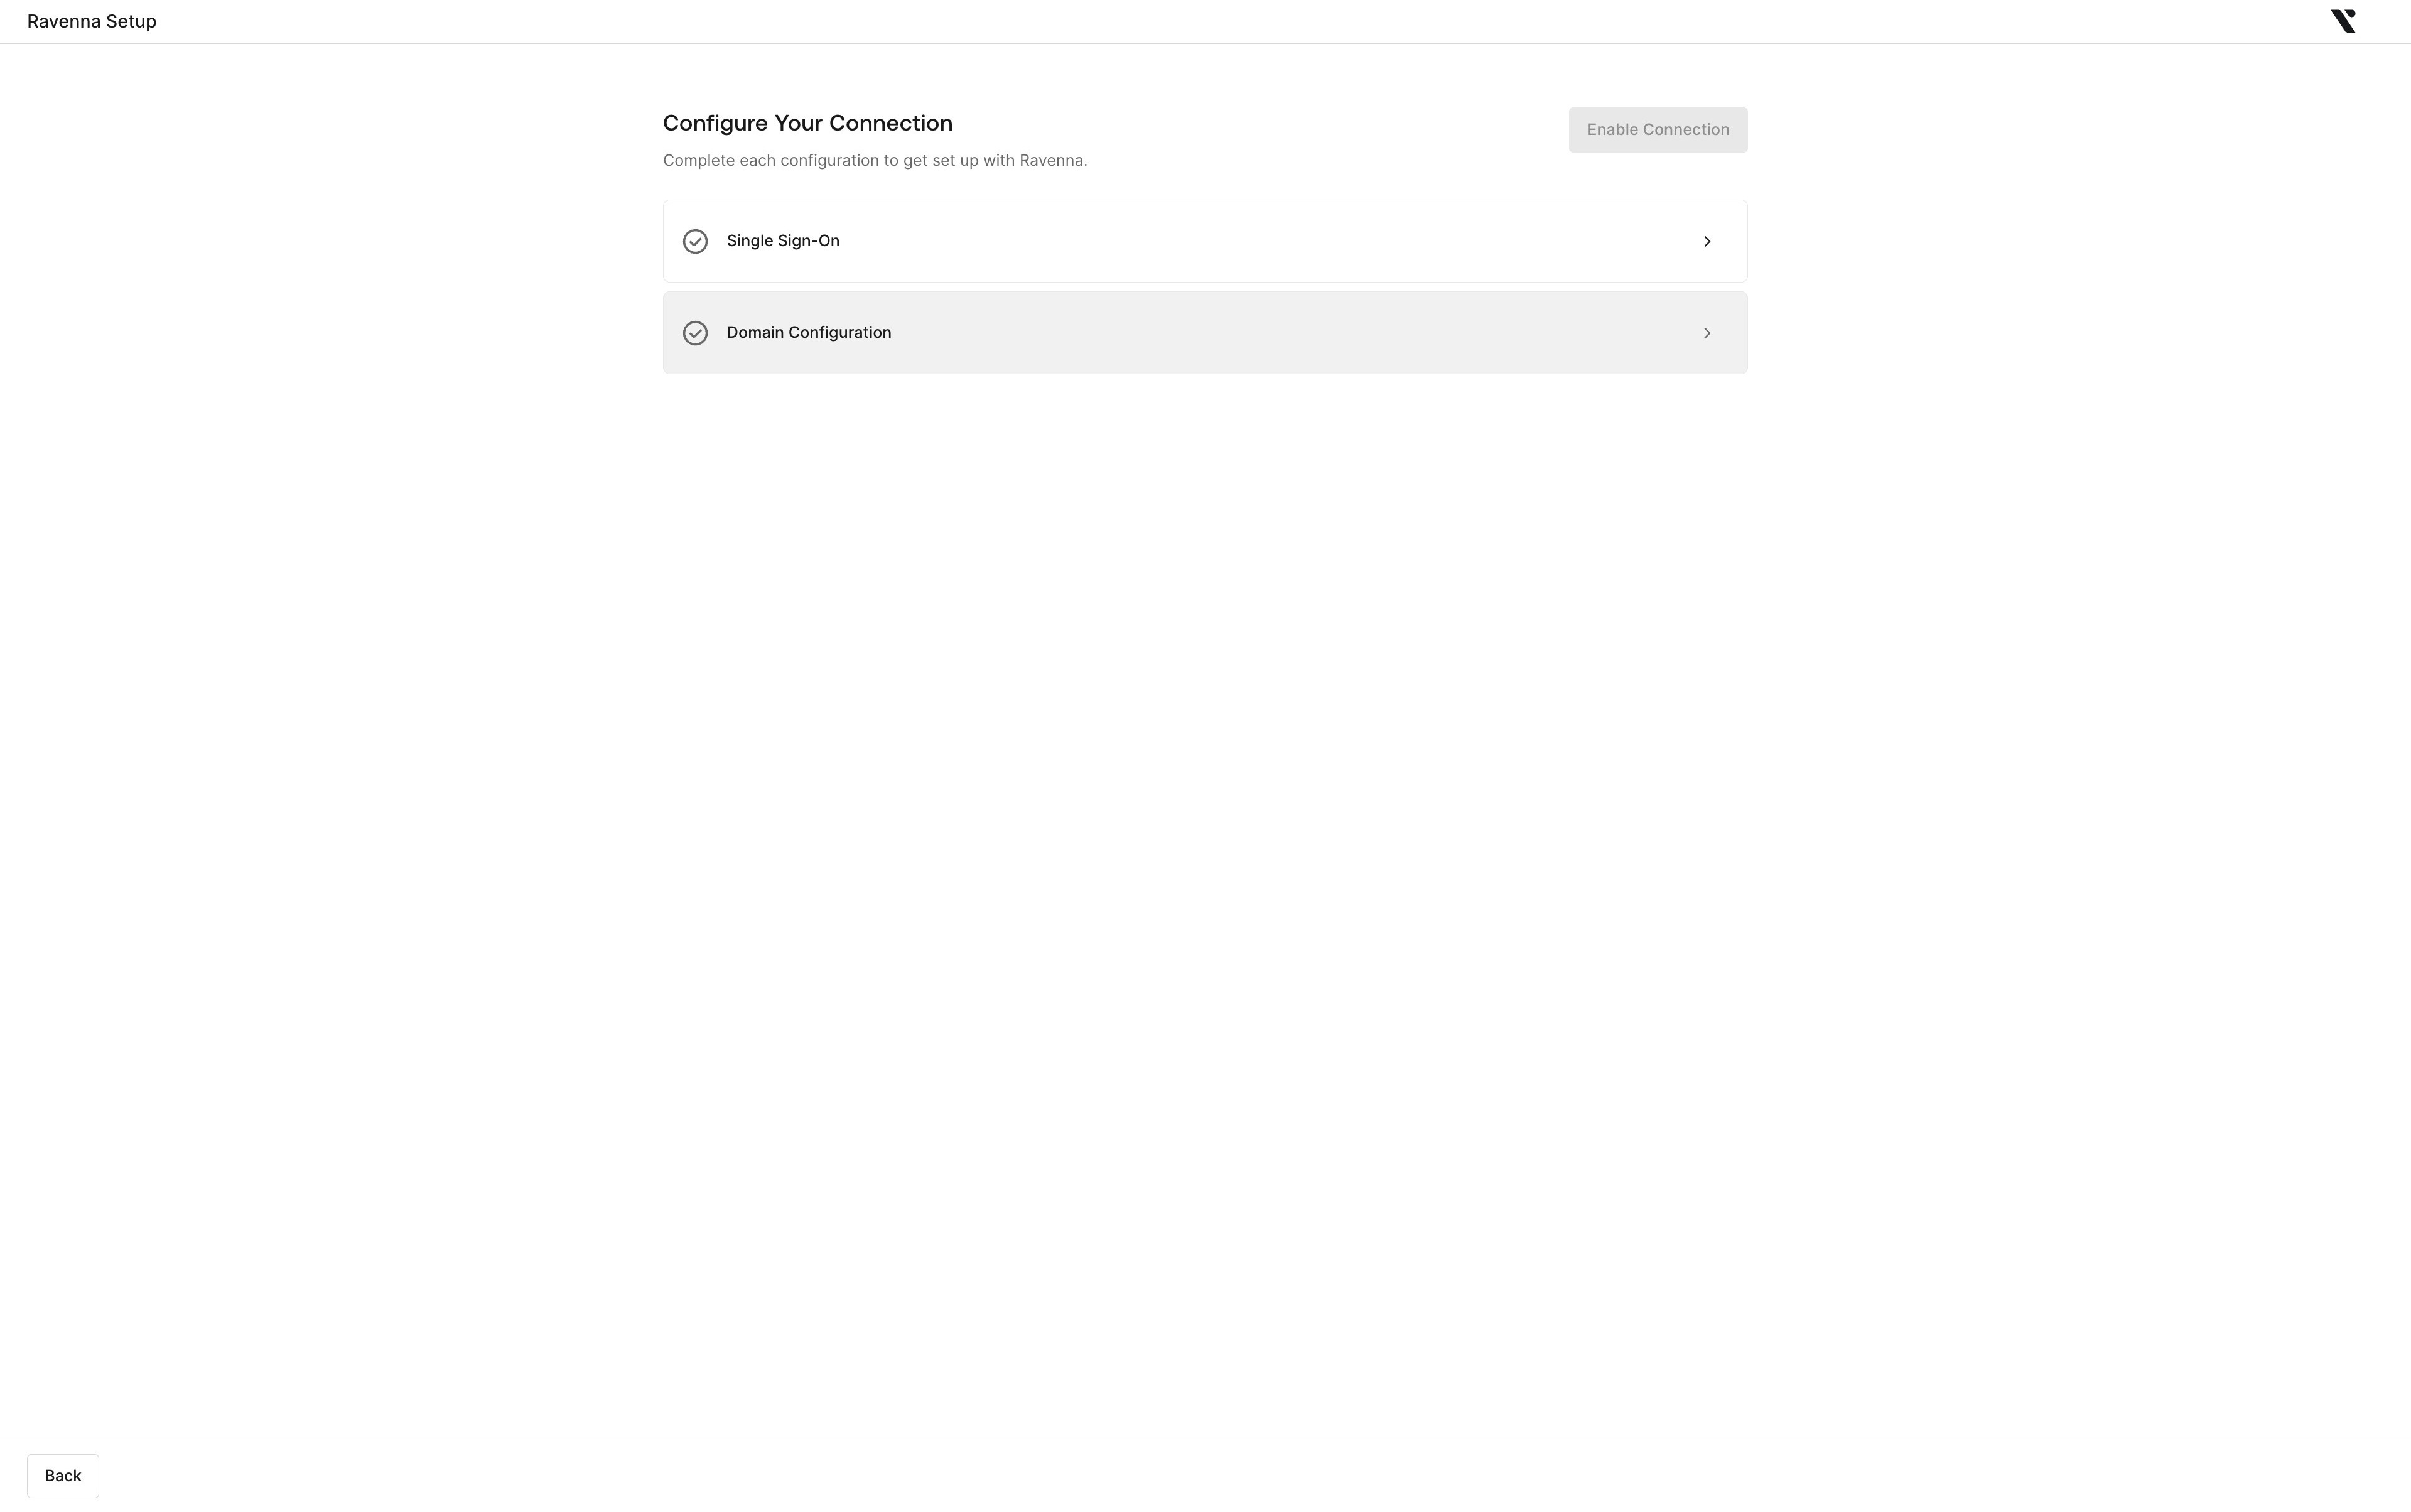
4
Select your identity provider
Select Okta, ADFS, Entra ID, Google Workspace, Keycloak, or PingFederate. For any other provider, select Custom SAML or Custom OIDC.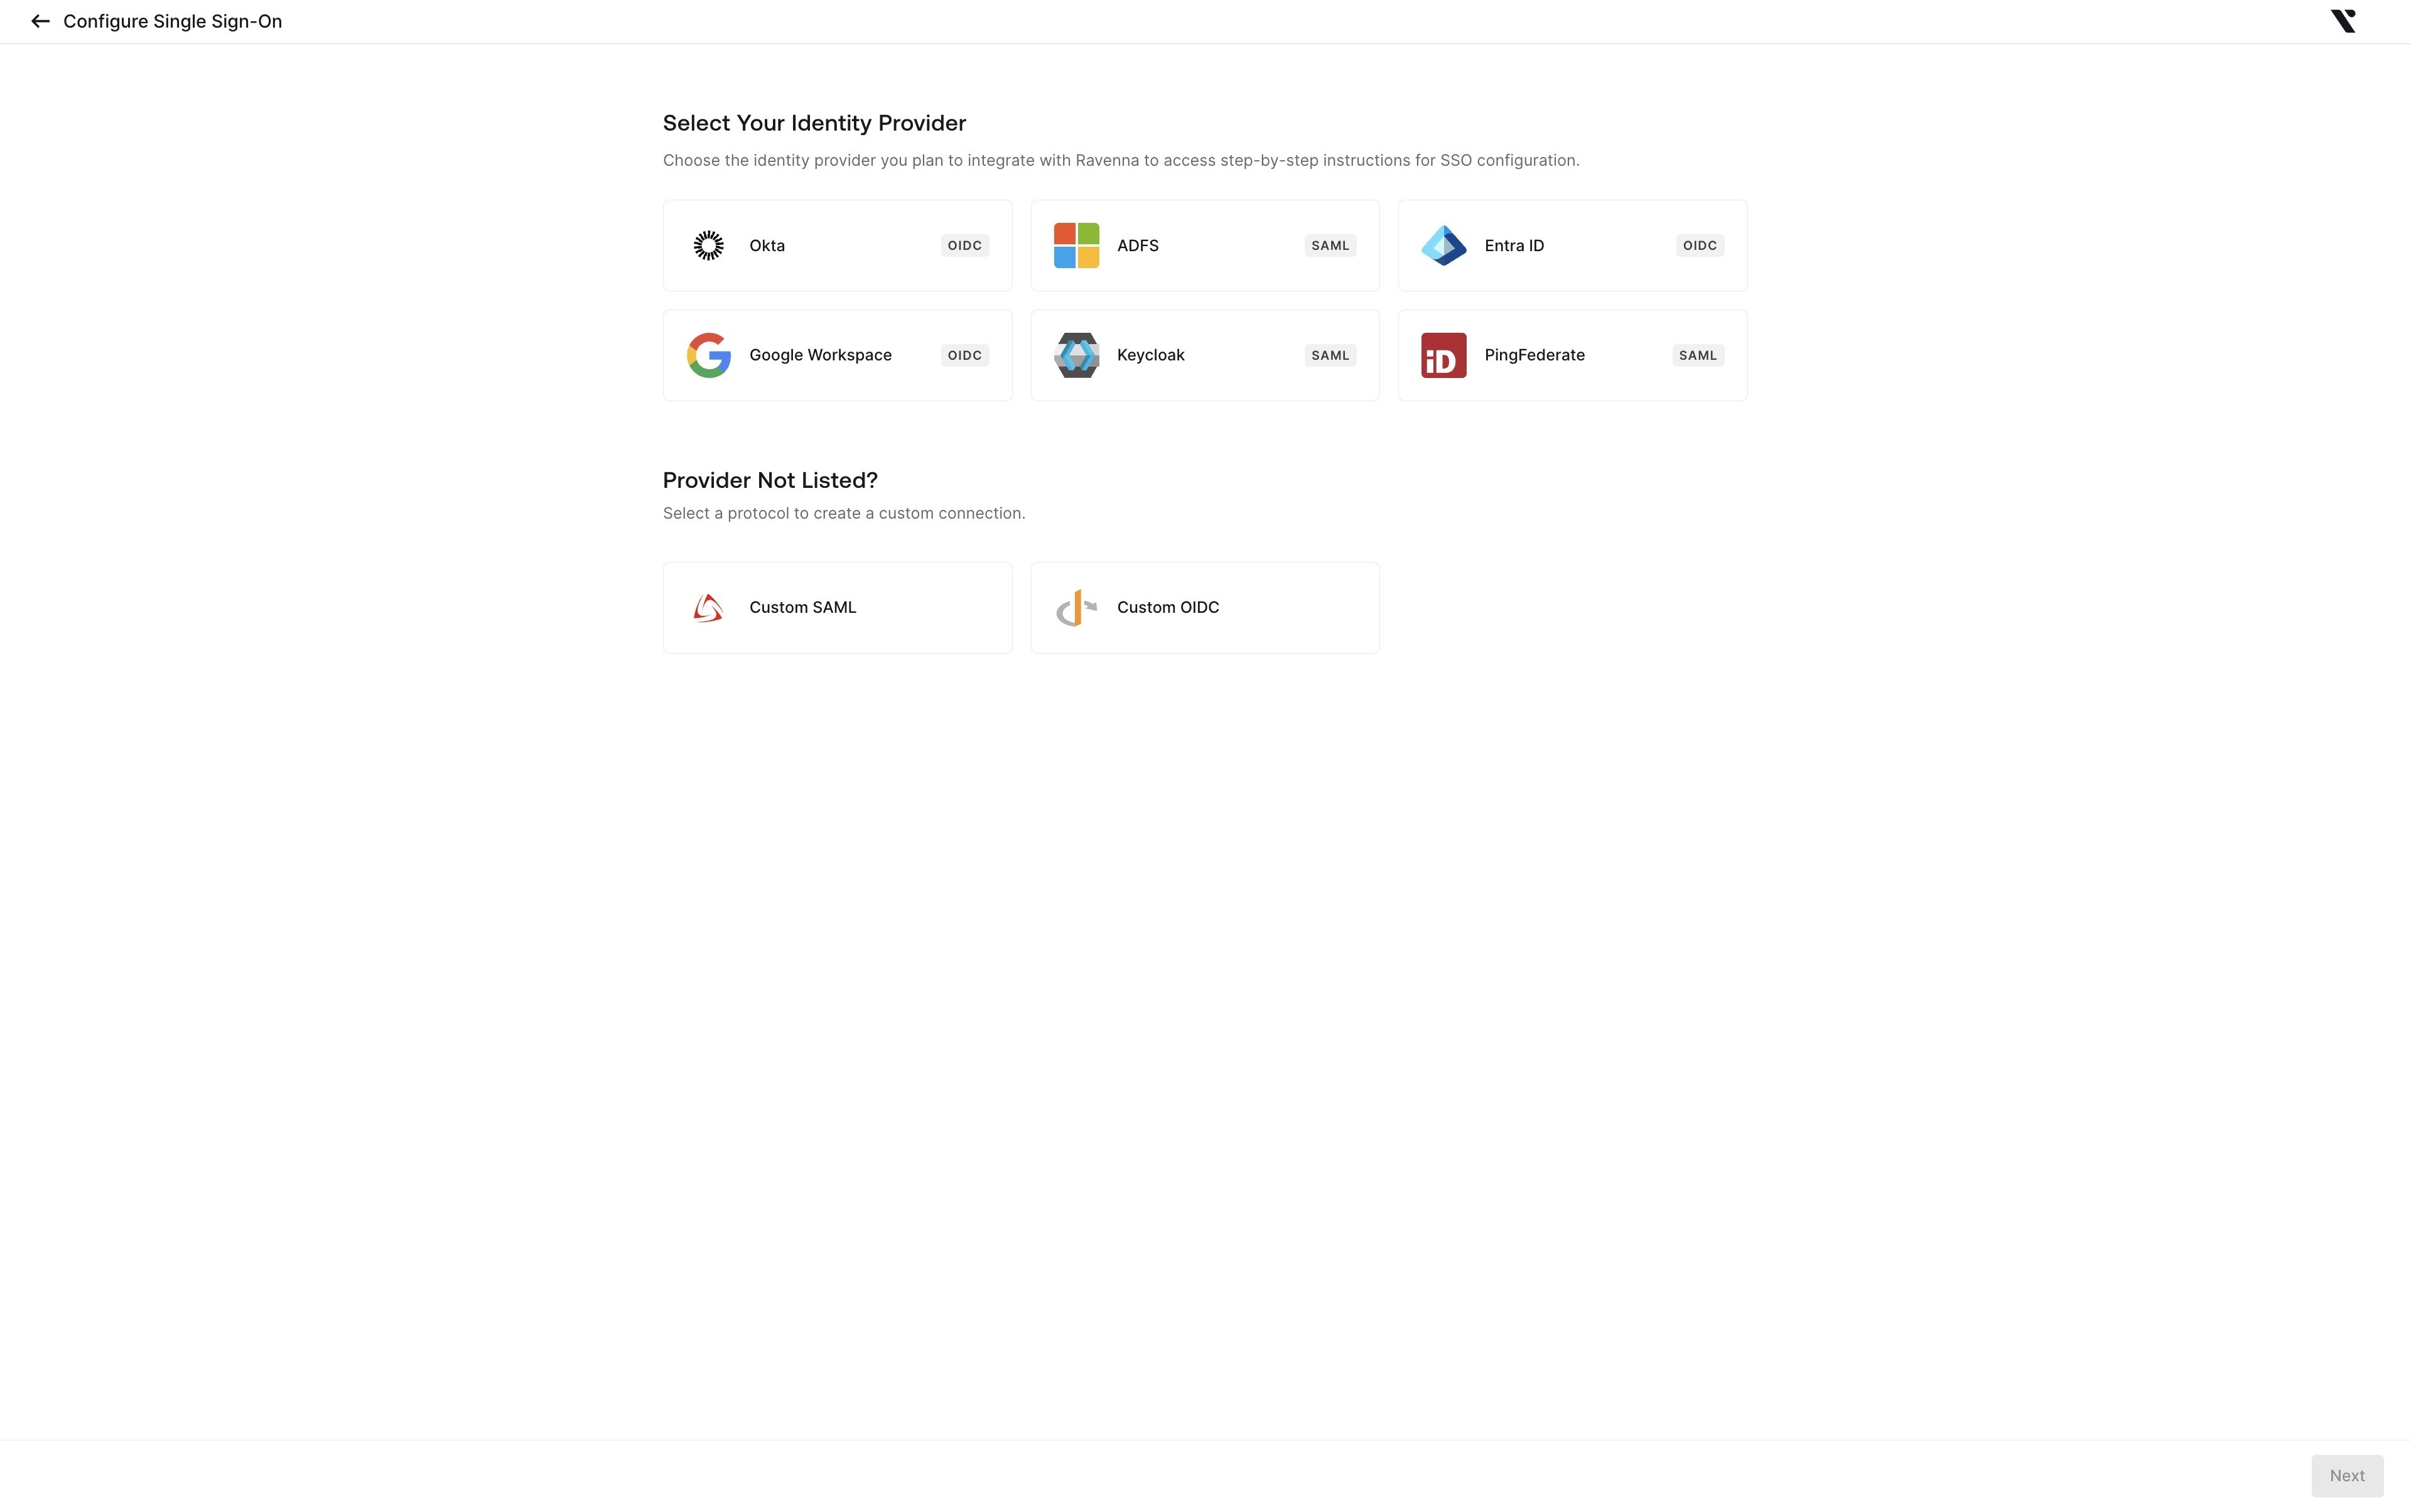
Configure your identity provider
The wizard shows the setup steps for the provider you selected, so step names and order vary. Complete each step in your IdP’s admin console, then click Next in the wizard.1
Create the application and enter its connection details
Follow the wizard’s instructions to create a Ravenna application in your IdP. Then copy the connection details from your IdP into the wizard.
2
Map claims, or skip if an integration syncs your users
Claims pass user attributes, such as first and last name, from your IdP to Ravenna when users sign in.If no connected integration syncs your users, add the claims the wizard lists to the Ravenna application in your IdP, then click Next.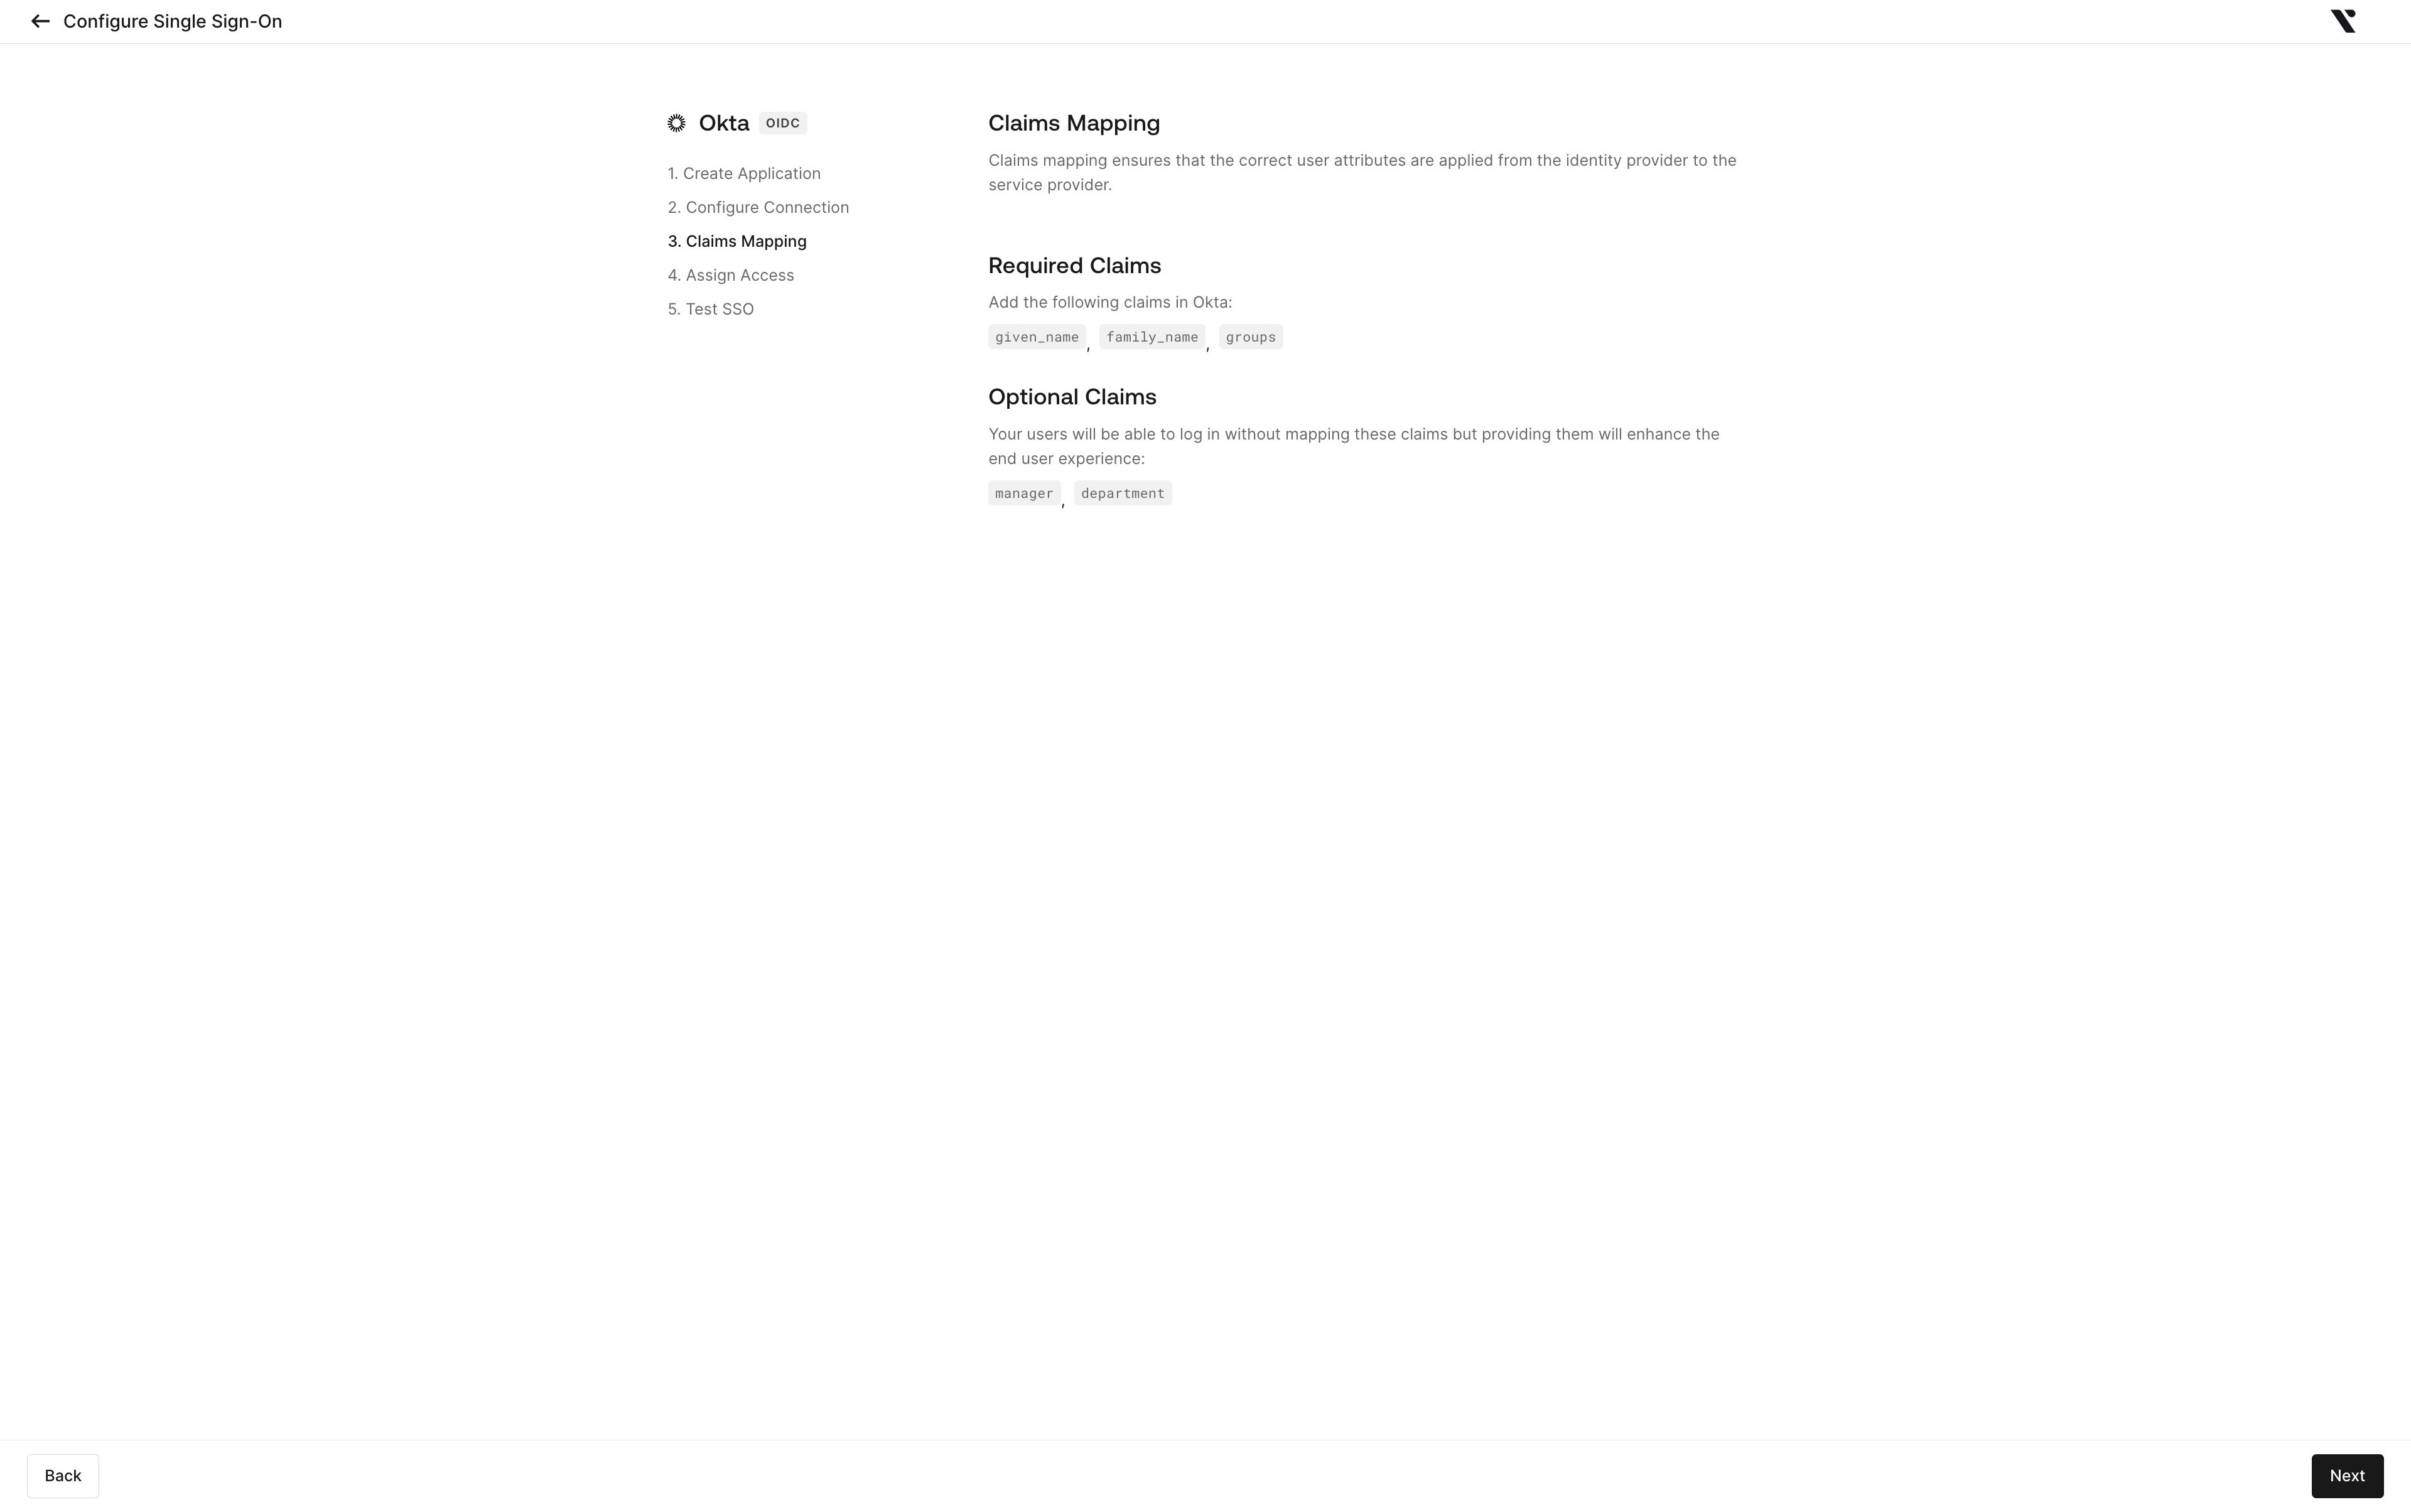
Tip: skip this step if an integration already syncs your users. If you’ve connected an integration that syncs user profiles, click Next without adding claims, even if the wizard marks them as required. The integration already imports names, managers, departments, and groups. This includes identity providers such as Okta, Microsoft Entra ID, Google Workspace, and JumpCloud, and HRIS integrations such as BambooHR, Rippling, and HiBob.
3
Assign access to users and groups
In your IdP, assign the Ravenna application to the users and groups who sign in with SSO. For example, in Okta, open the application’s Assignments tab, select Assign > Assign to Groups, click Assign next to each group, then click Done.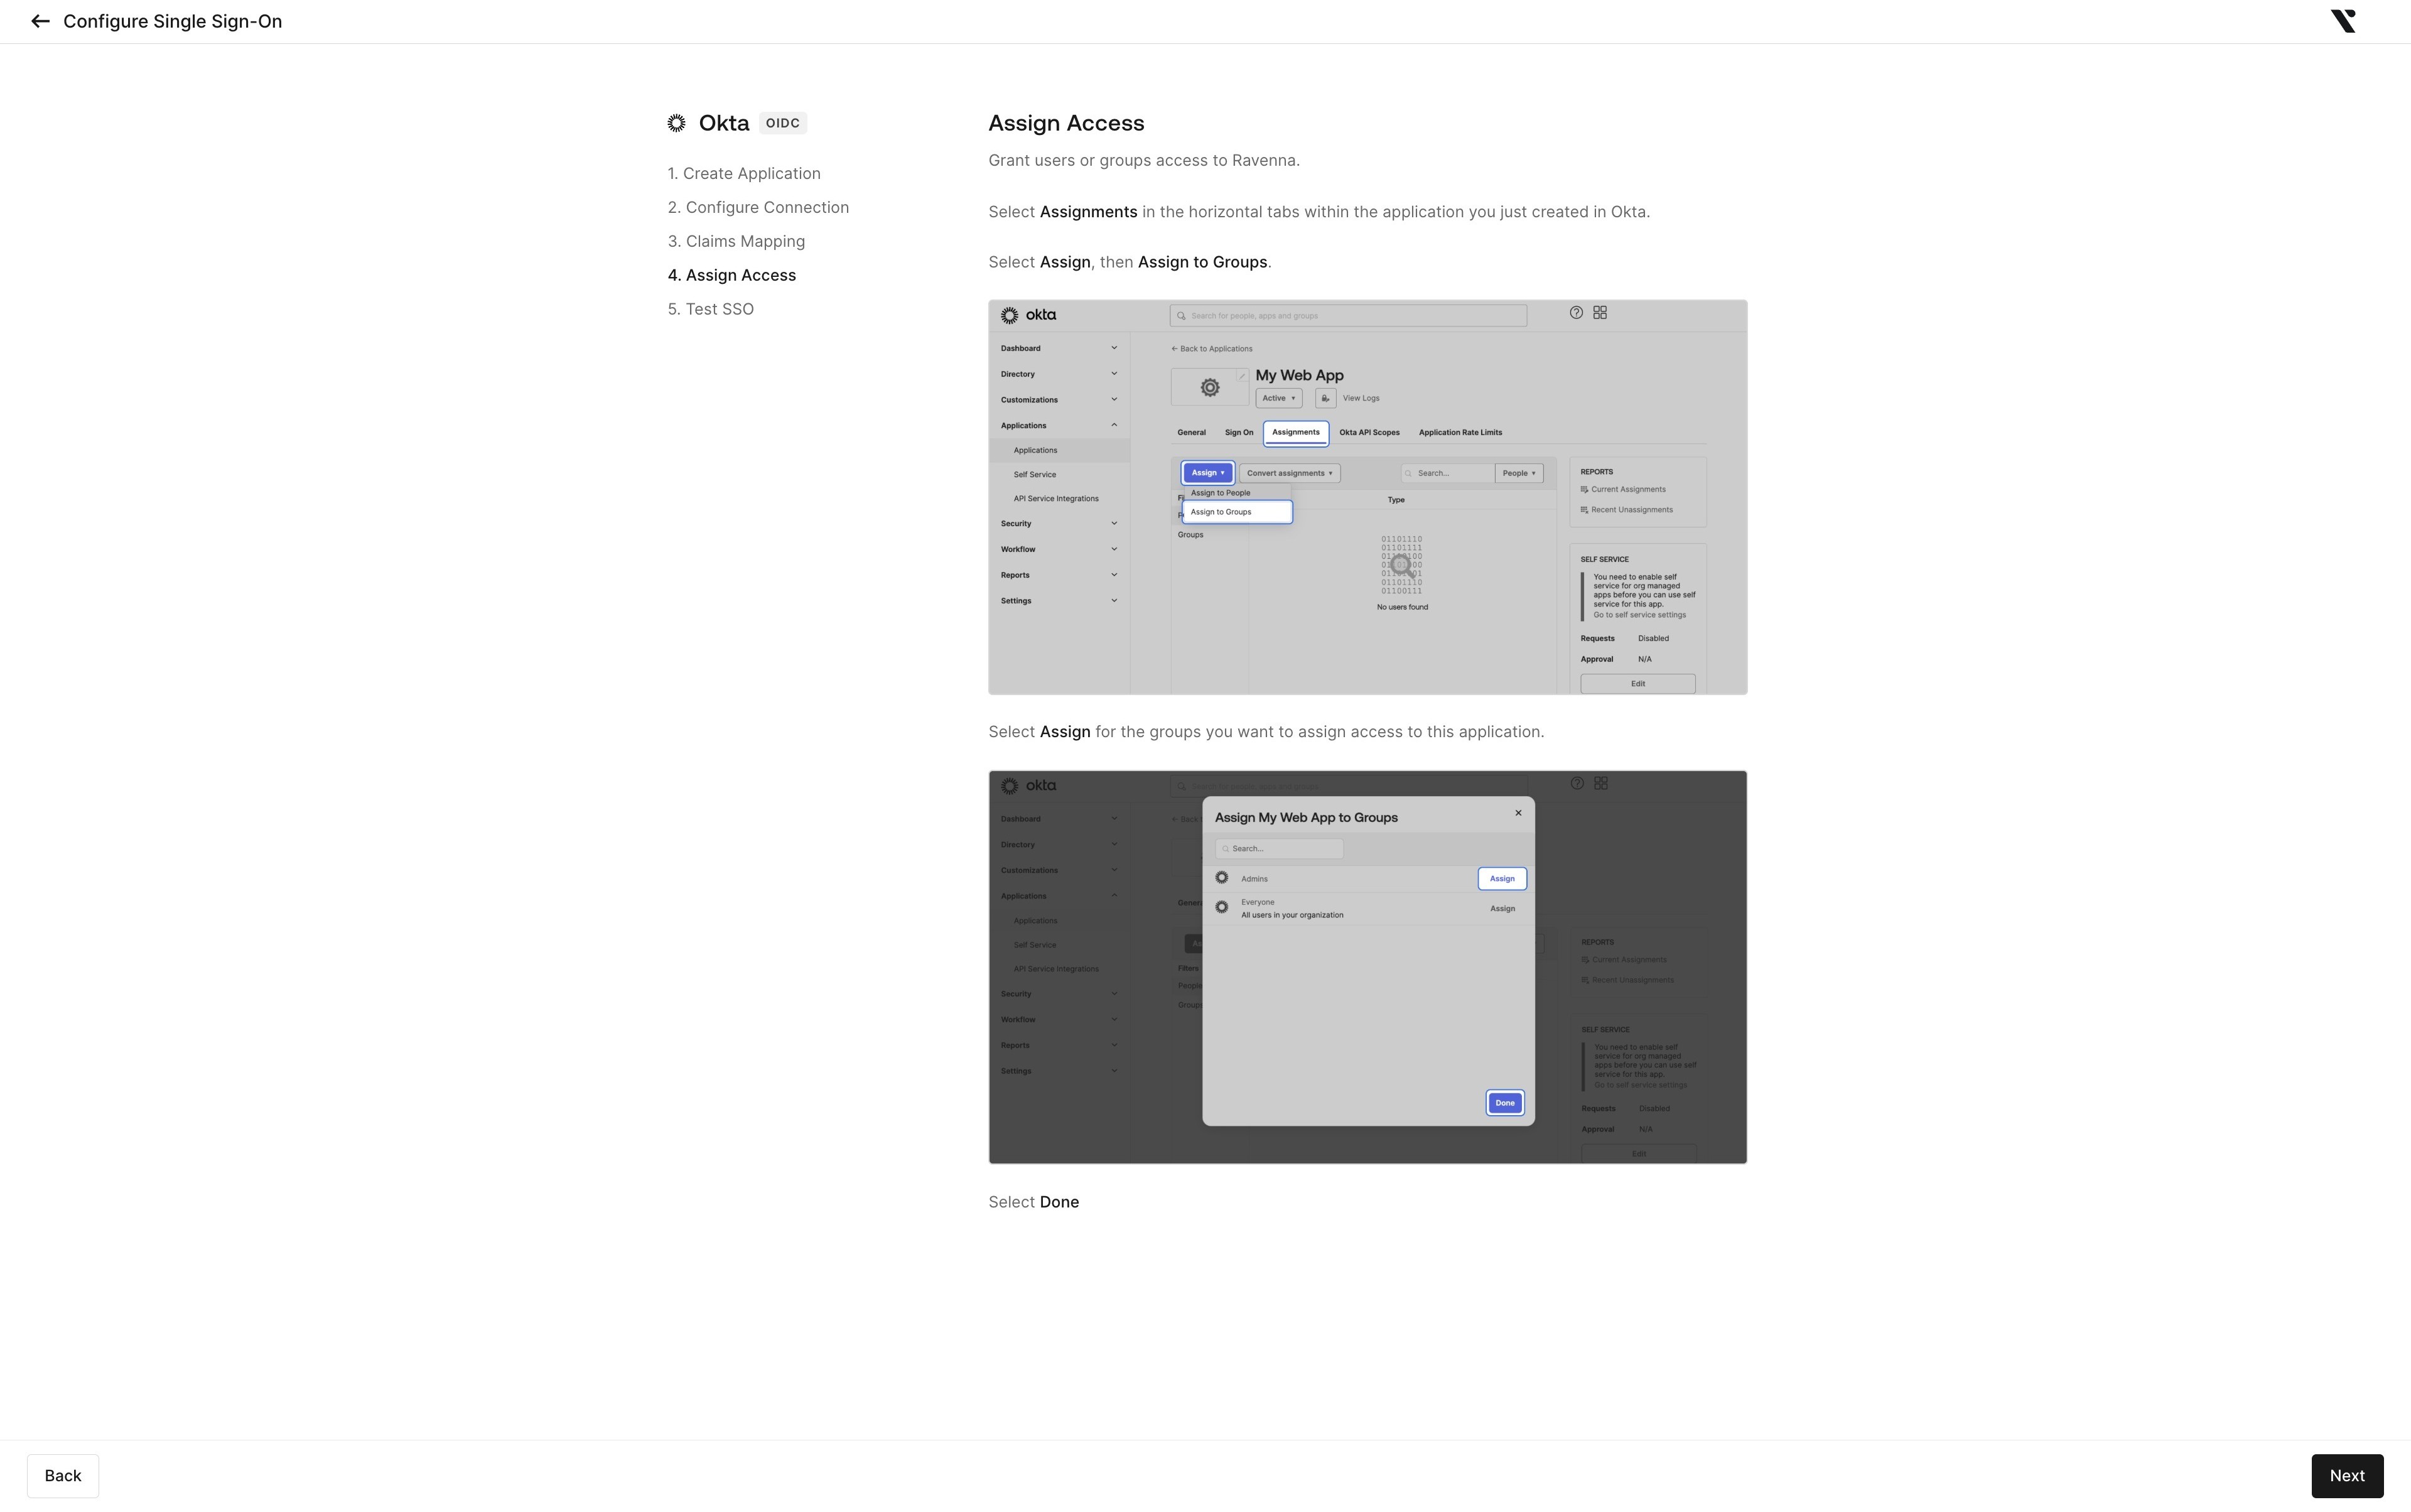
4
Test the connection
Click Test Connection. A new window opens and signs you in through your IdP, the same way your users sign in. Keep the wizard open while the test runs. If the test fails, the wizard lists the errors.When the test succeeds, click Done.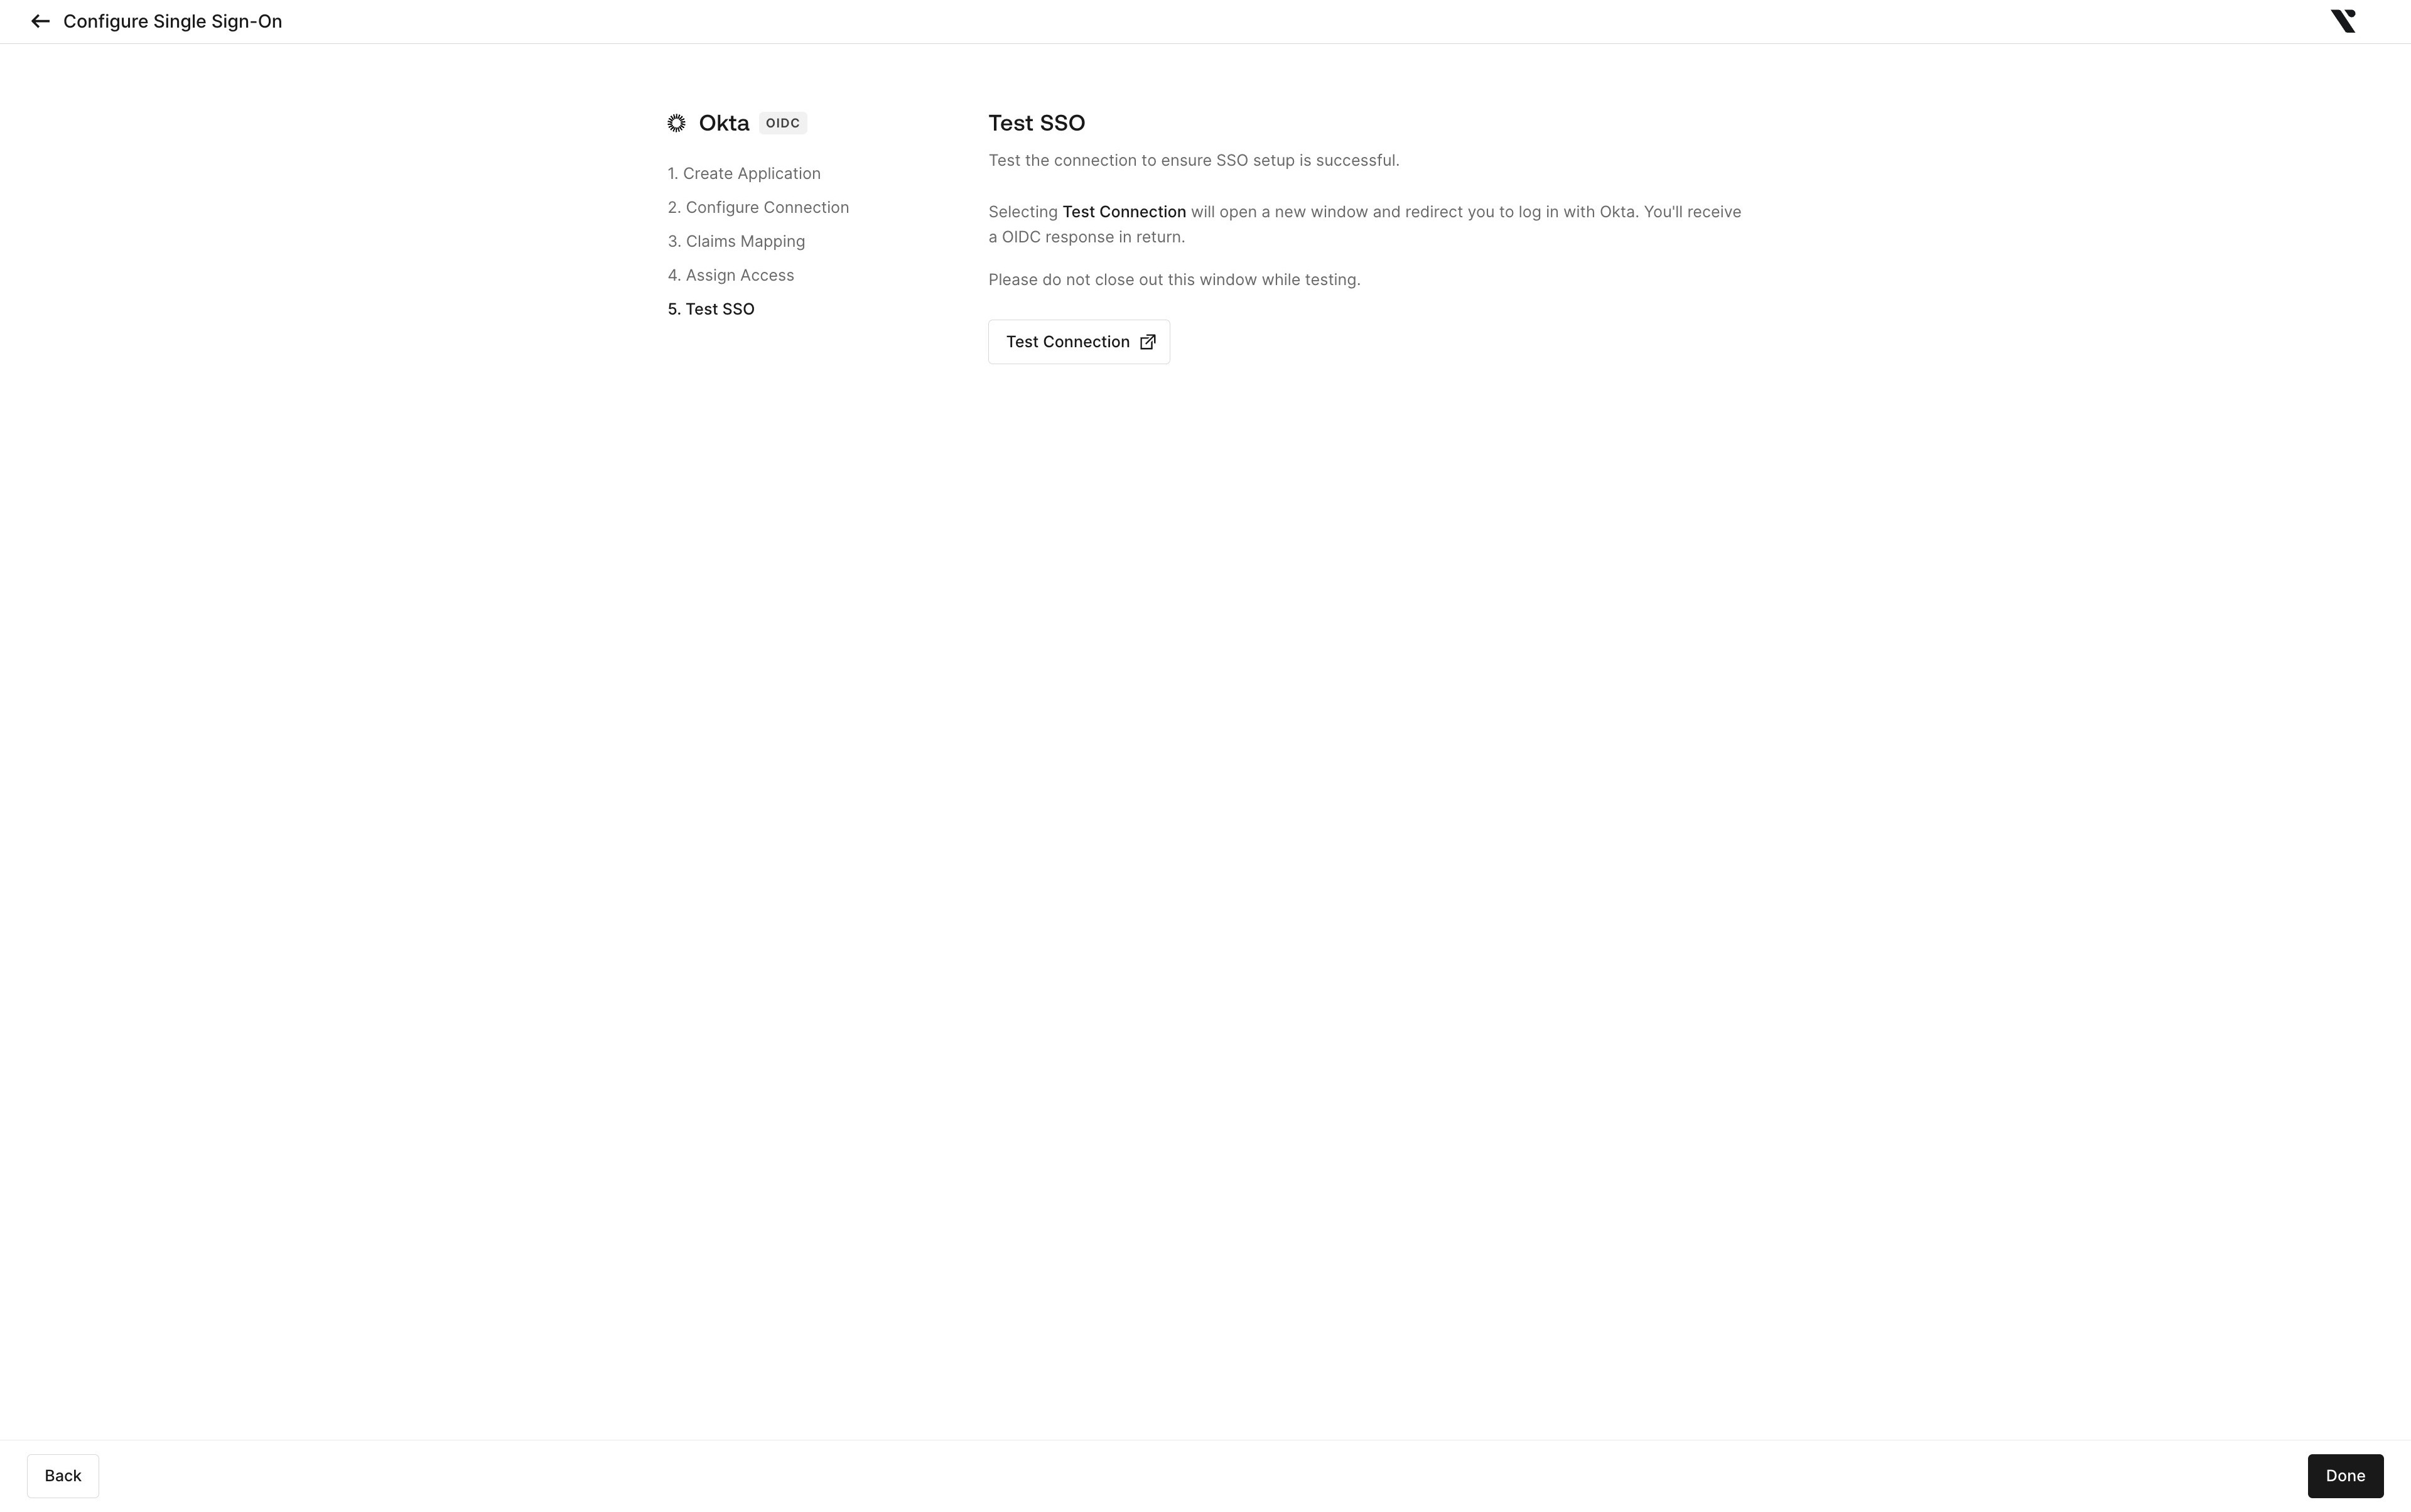
Verify your domain Optional
On Configure Your Connection, you can also select Domain Configuration to add and verify the email domains your users sign in with. To skip this, go to Enable the connection.1
Add your domain
Select Domain Configuration, enter your email domain, and click Add Domain.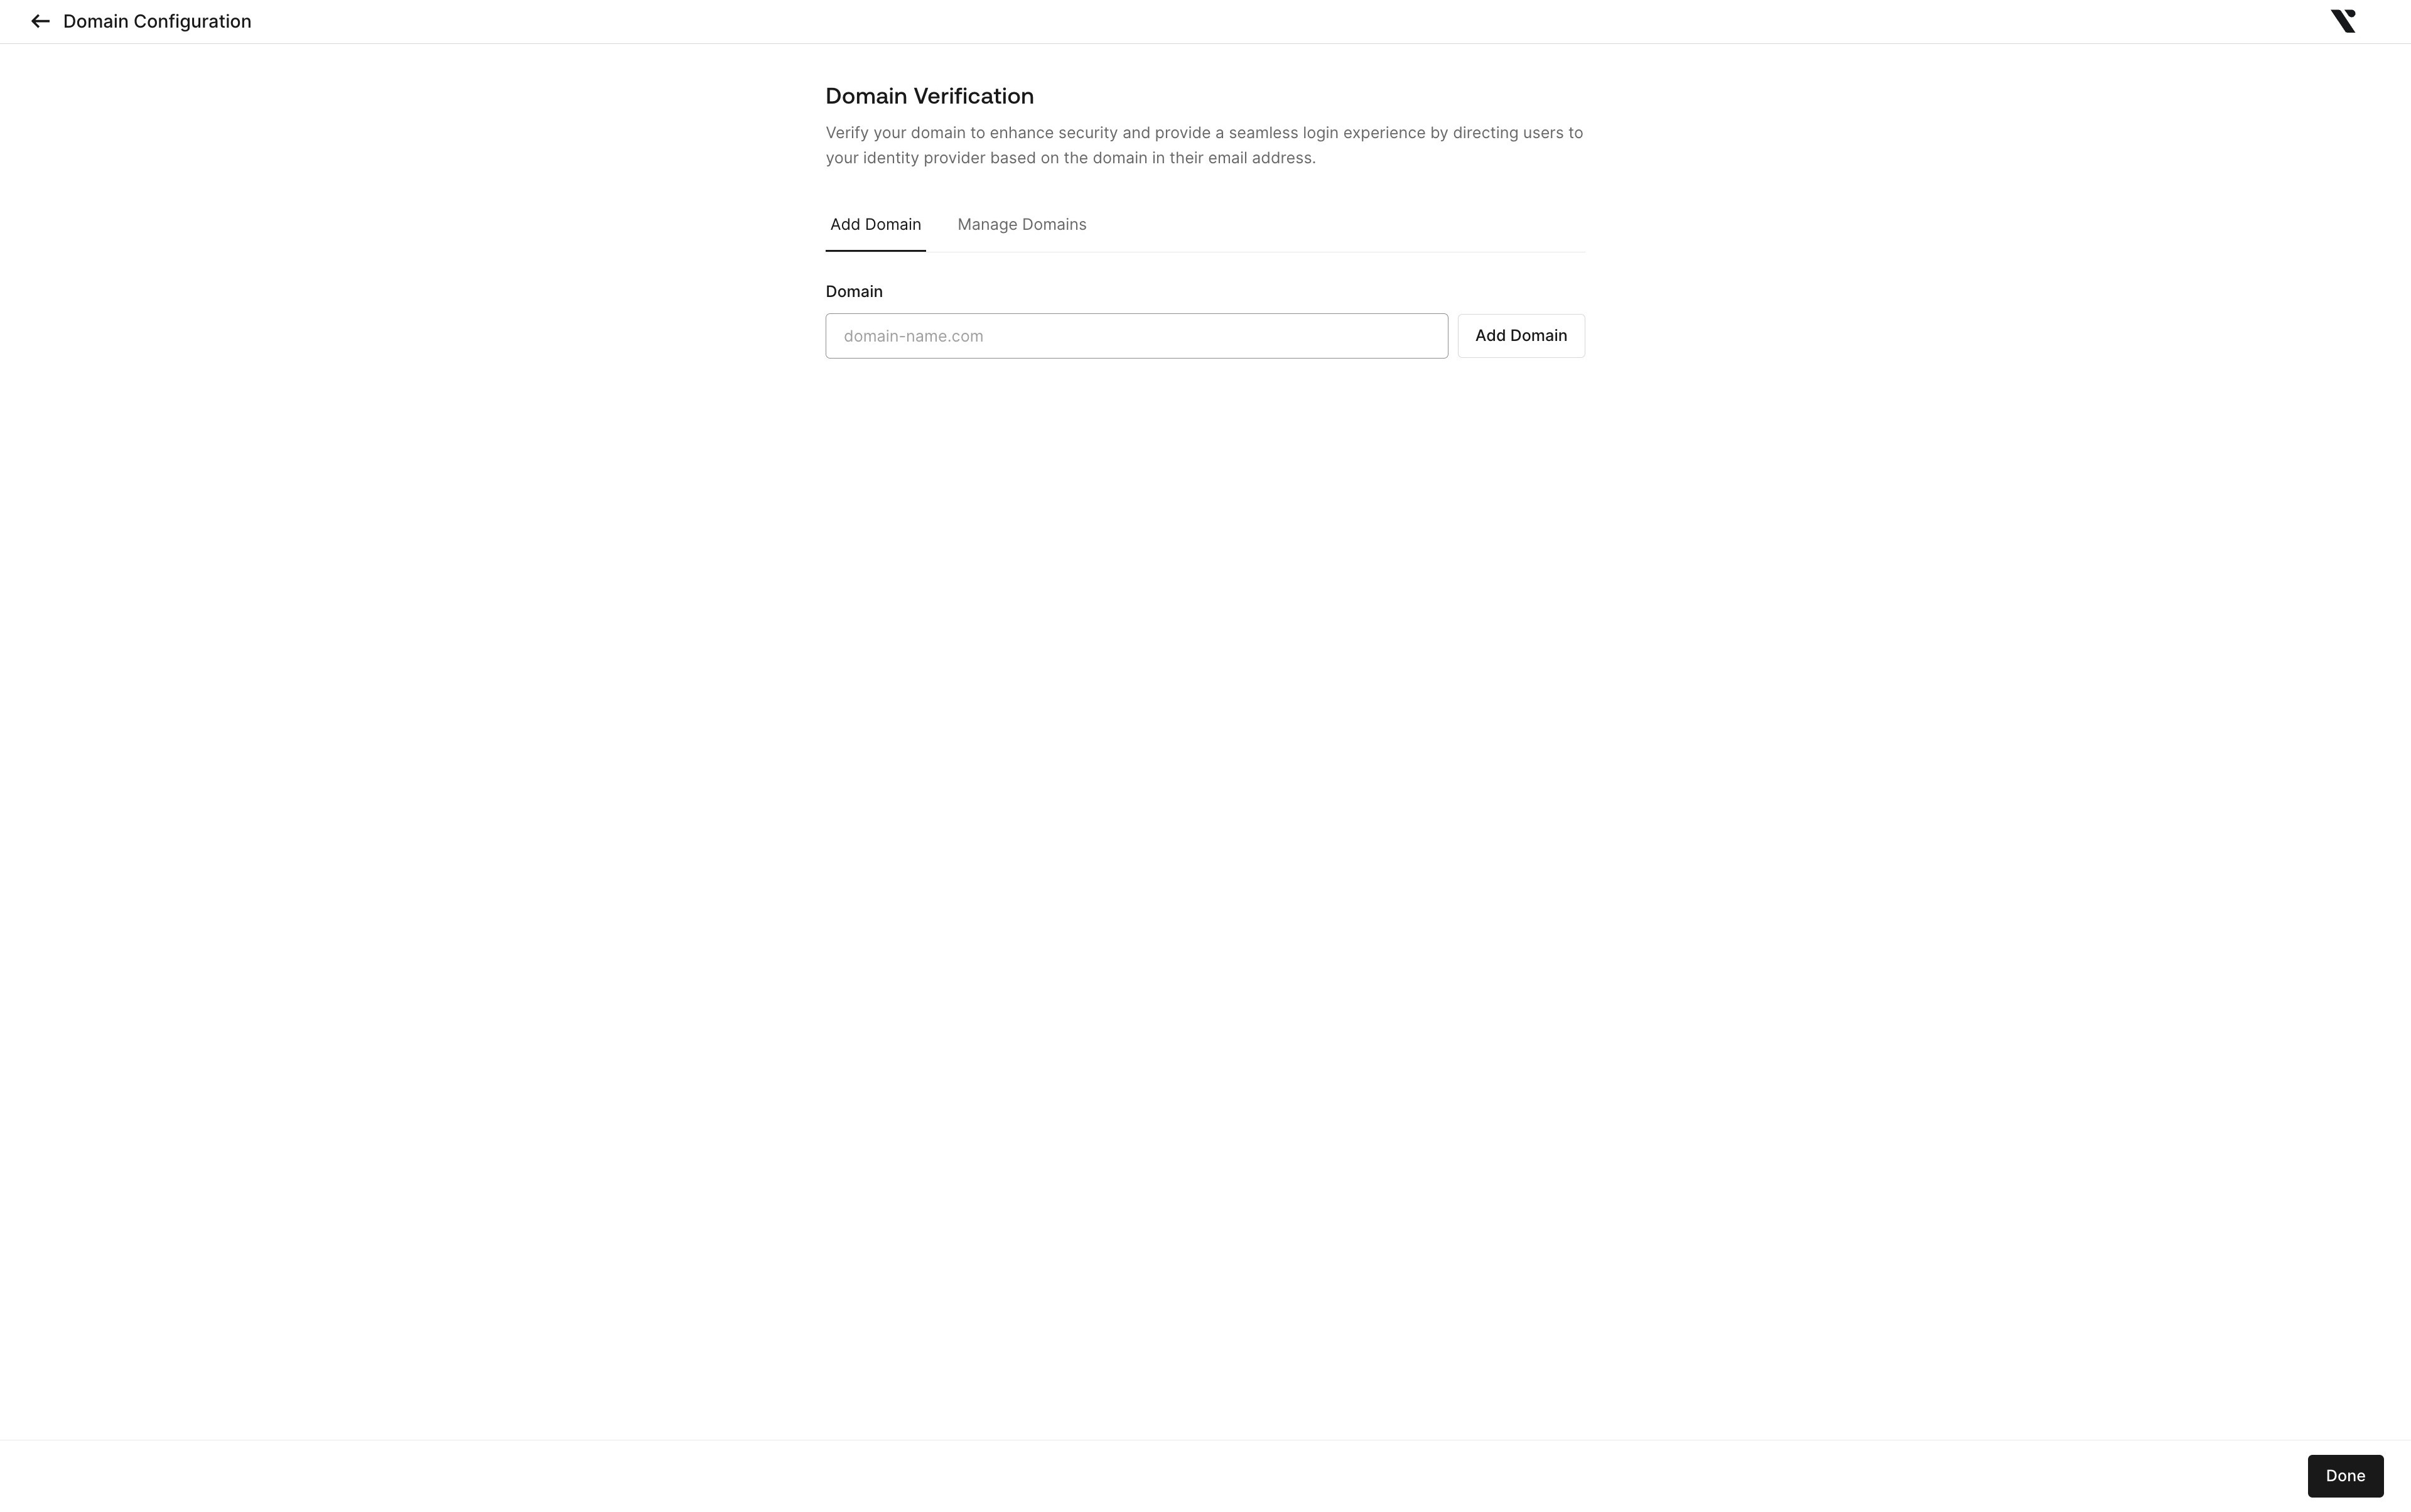
2
Add the TXT record and verify
Under Pending Domains, select your domain to see its TXT Record Name and TXT Record Content. Add a TXT record with those values in your domain’s DNS settings, then click Verify. DNS changes can take up to 48 hours.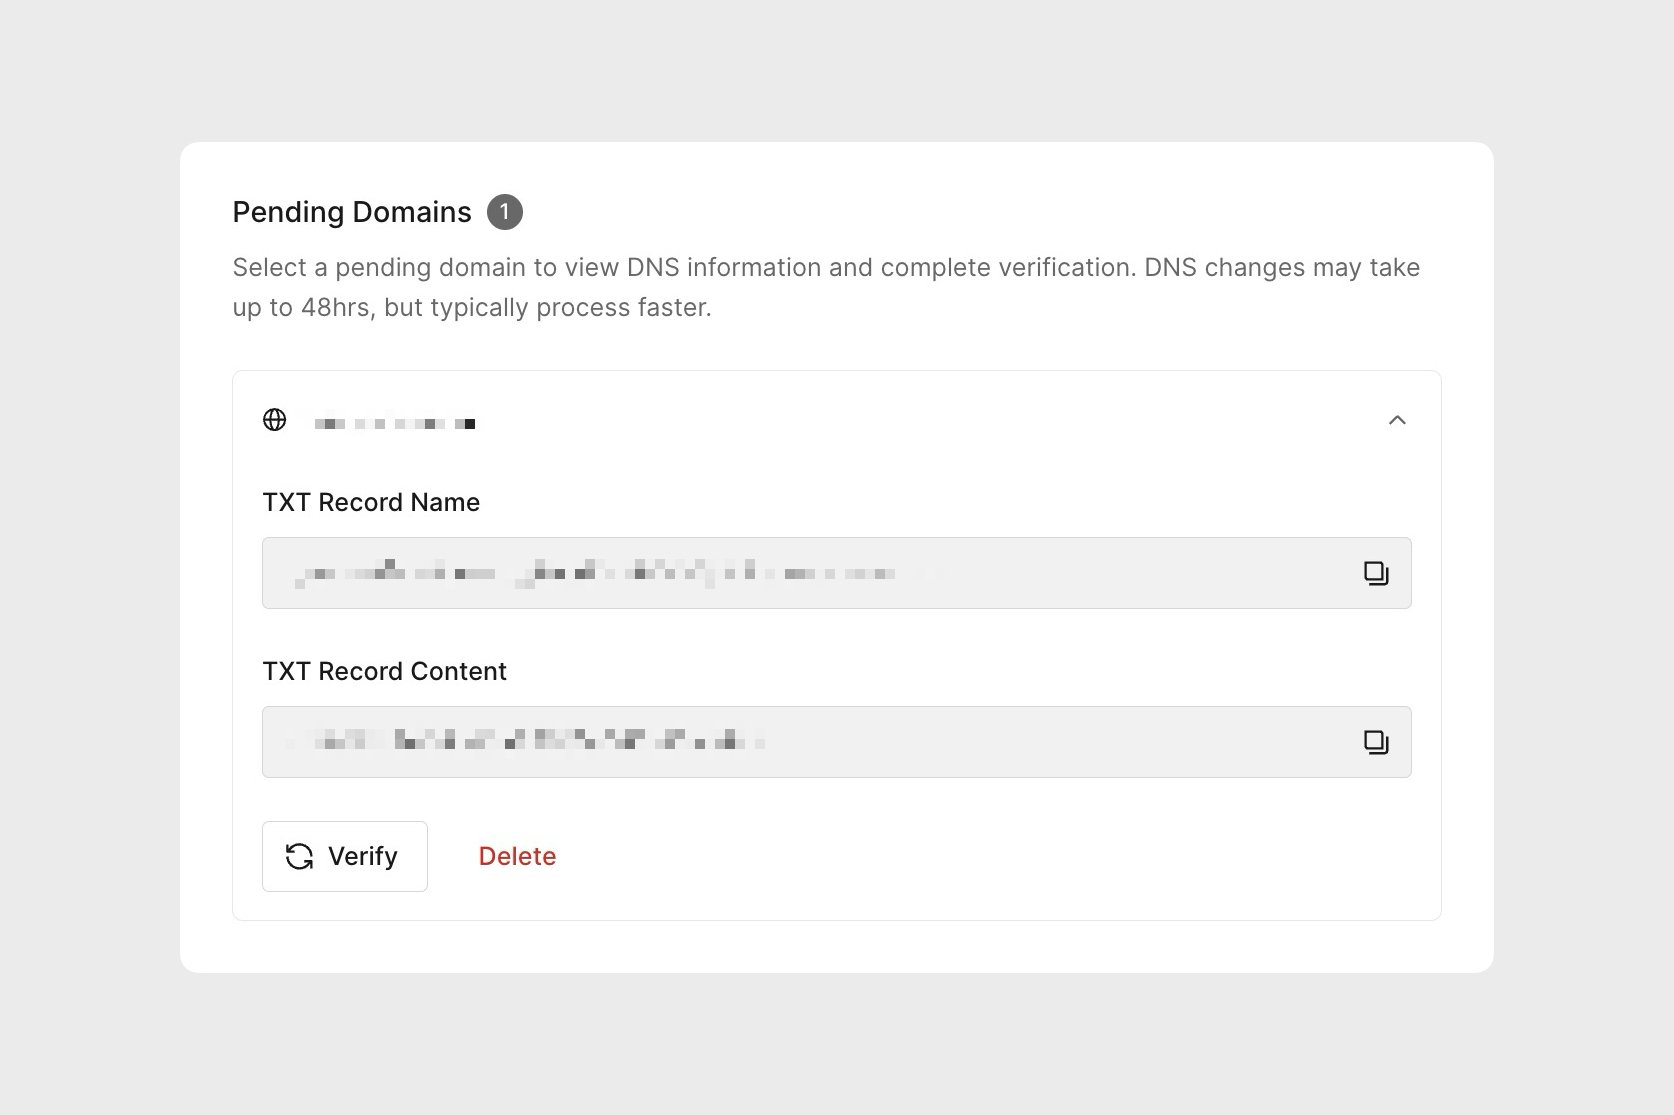
Enable the connection
1
Click Enable Connection
On Configure Your Connection, click Enable Connection in the top right. The button becomes available once Single Sign-On is complete.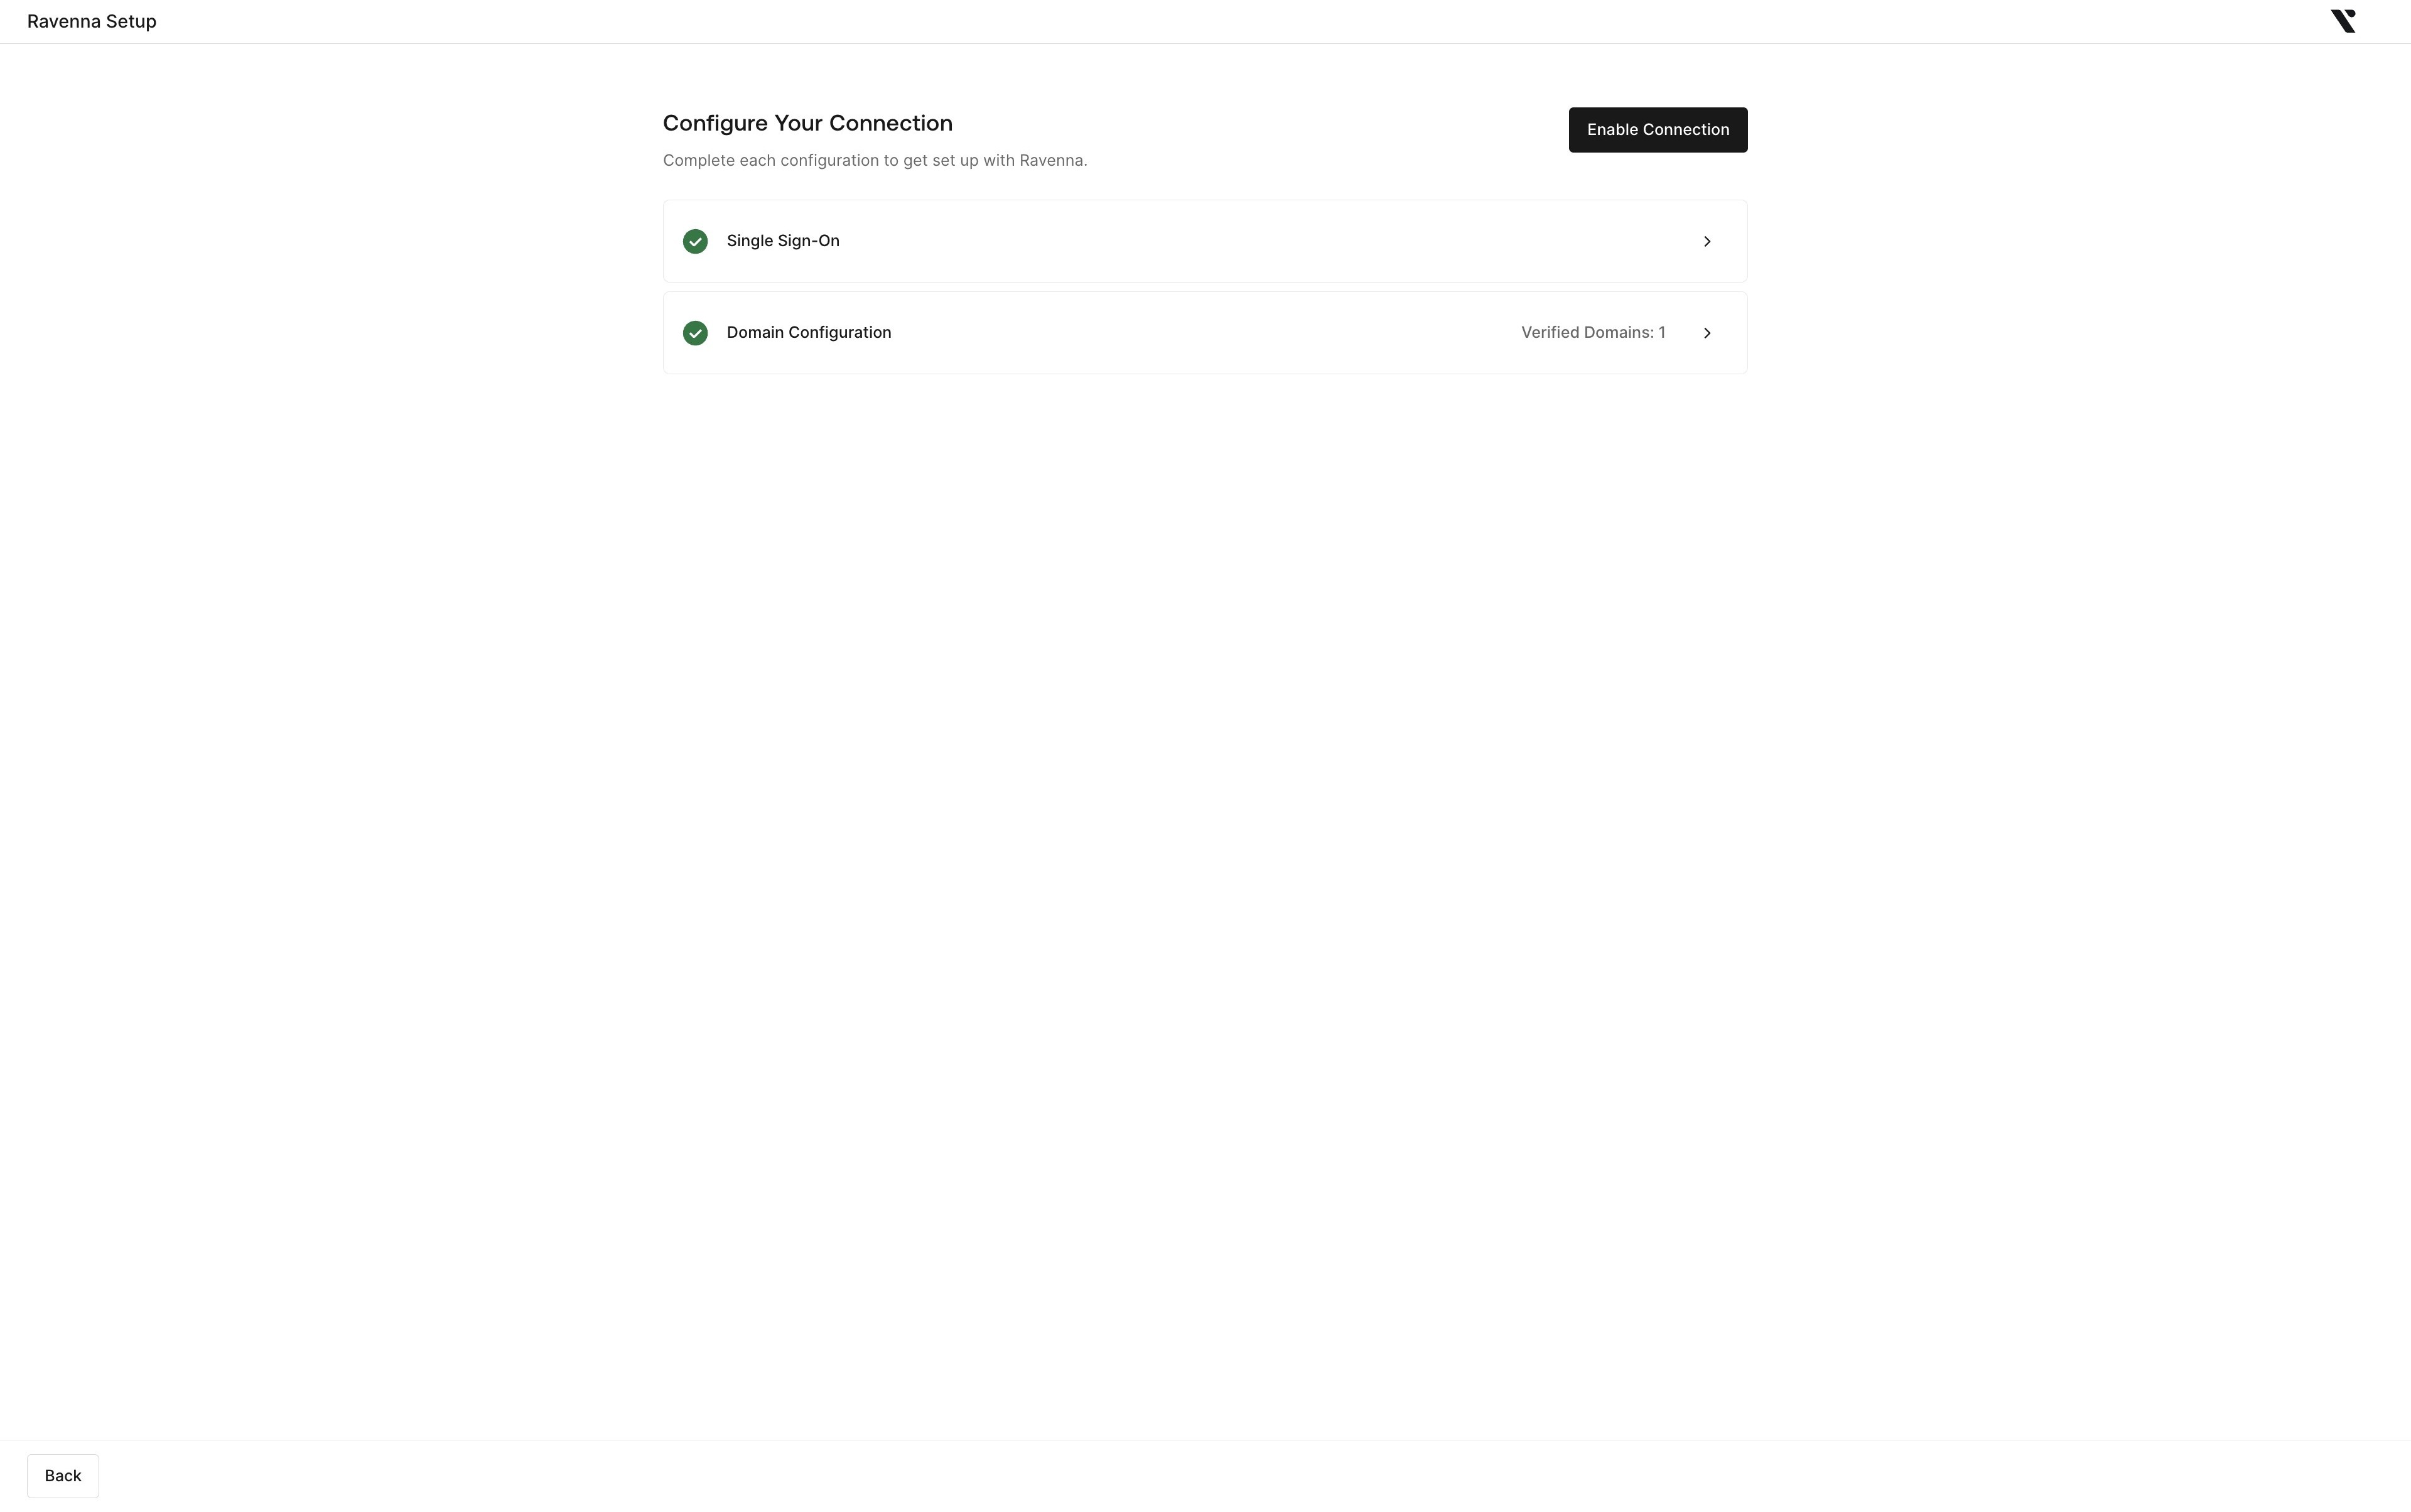
2
Confirm and proceed
The wizard asks you to confirm that you’ve assigned access to users. Click Proceed.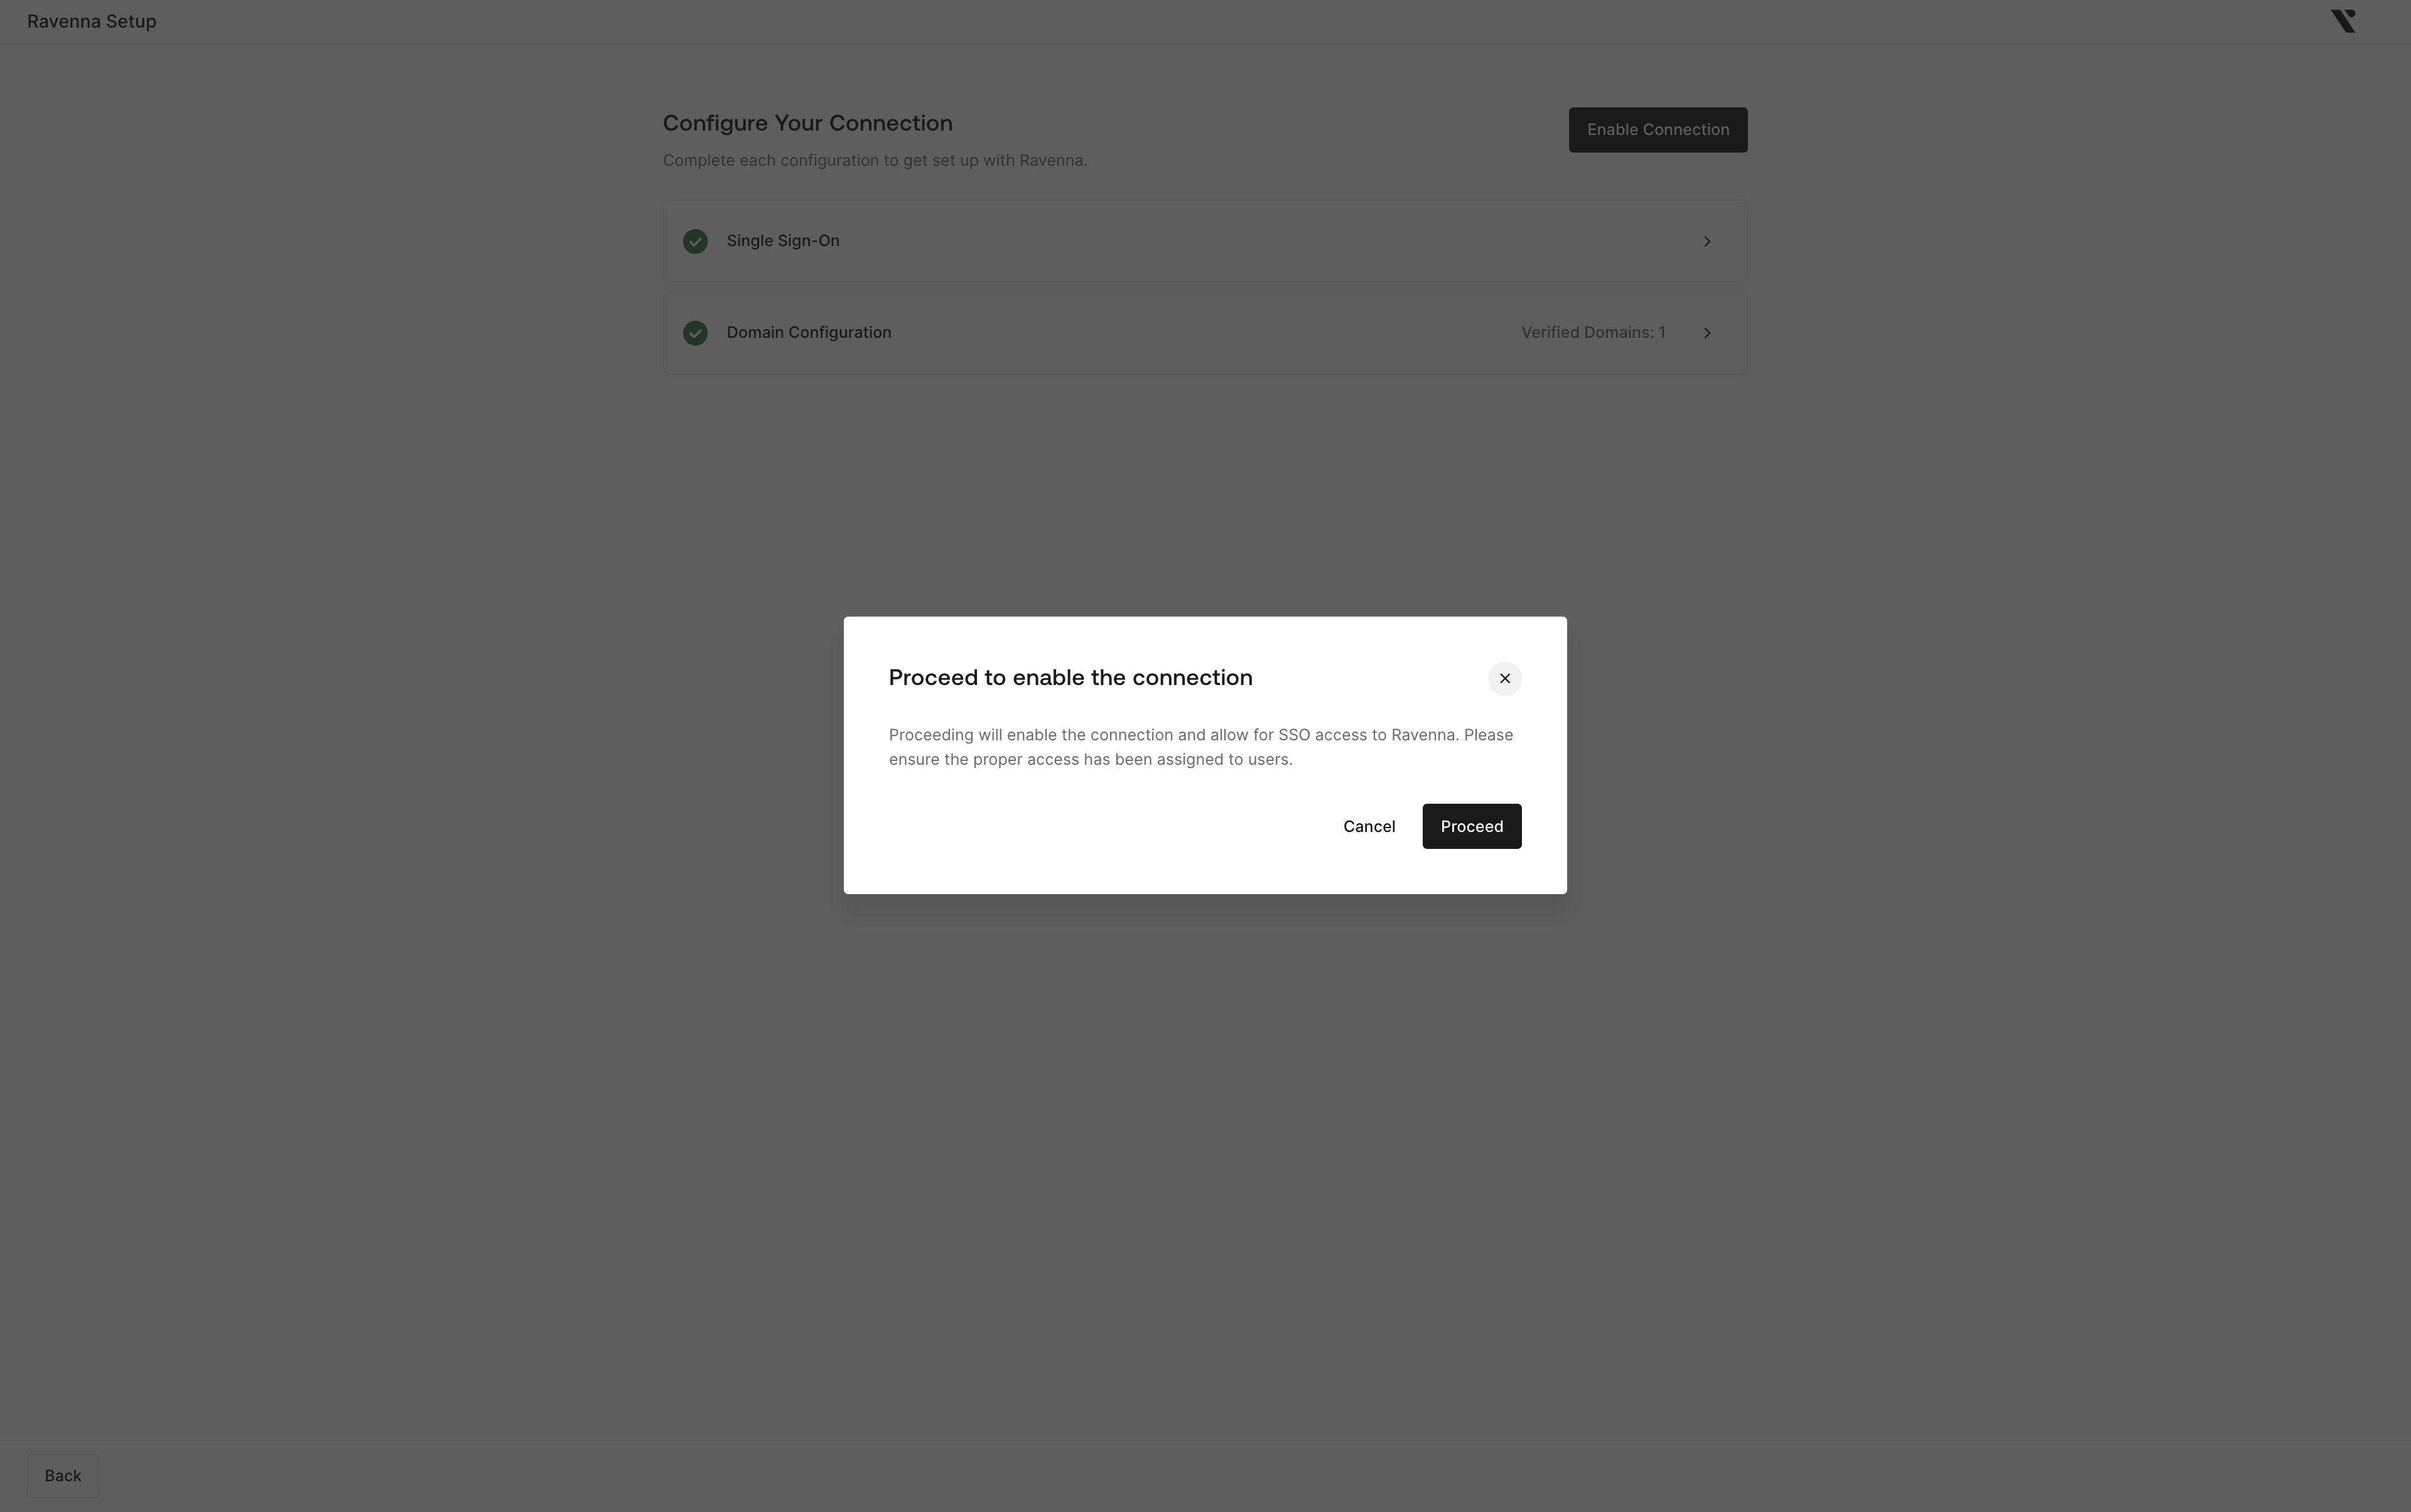
3
Close the confirmation page
The wizard confirms that the connection is enabled. Close the tab.
4
Confirm the connection in Ravenna
Go back to Settings > SSO. Your IdP shows as Connected, with your organization’s SSO Login URL below it.Enforce SSO-Only Authentication shows Enforced if no other sign-in methods are turned on, which is the default. See Enforce SSO-only sign-in.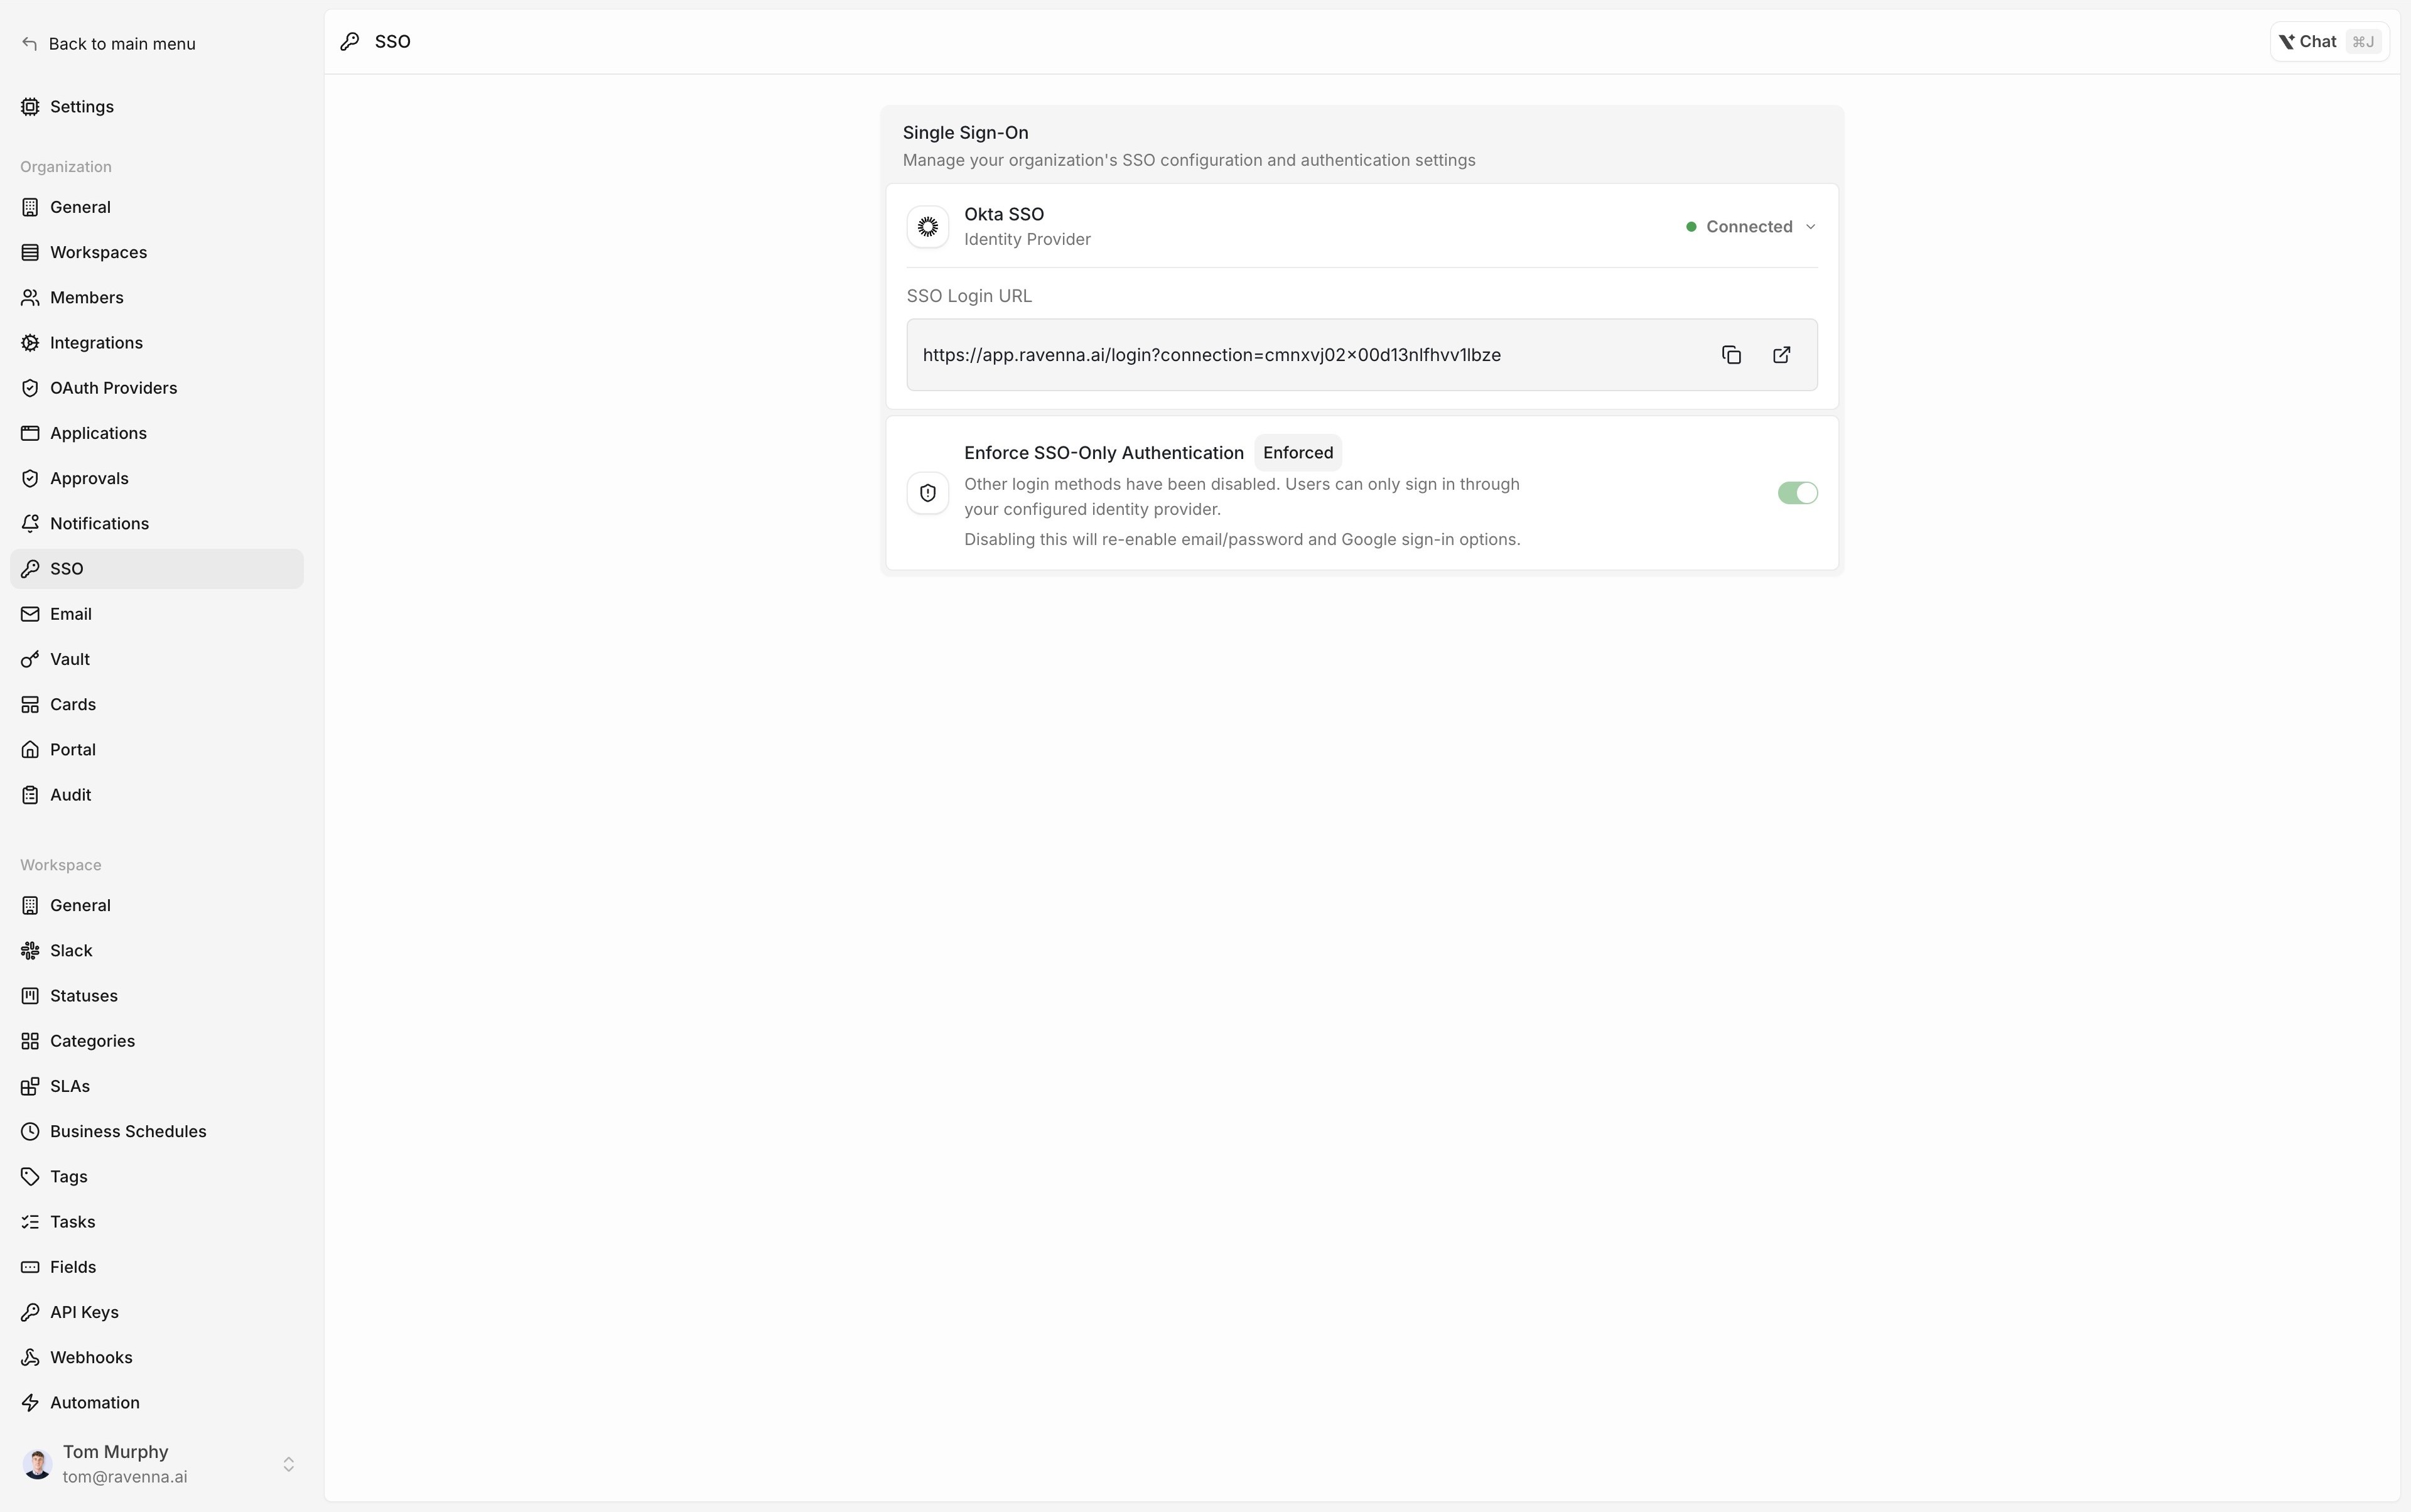
Roll out SSO to your team
Users now sign in by entering their work email on the Ravenna login page and clicking Continue. Ravenna recognizes your organization’s email domain and sends them to your IdP. To give them one-click access, add the direct SSO login URL to your IdP’s app portal.Direct SSO login URL
The direct SSO login URL skips the email step and opens your IdP directly. Copy it from SSO Login URL on Settings > SSO. It looks like this:Add the URL to your IdP portal
Set the URL as the login or home page URL of the Ravenna application in your IdP.- Okta
- Microsoft Entra ID
- Google Workspace
- JumpCloud
 Okta
 Microsoft Entra ID
 Google Workspace
 JumpCloud
Go to Applications > your app > General and paste the URL into Login URL.
Next steps
User management
Give SSO users roles and workspace access.
Manage SSO
Edit, disconnect, or delete your connection.
Troubleshooting
Fix a failed test or sign-in errors.